CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 09 Title: Passwords - A Cracking Christmas Bonus: Side Quest 2 Key Challenge |
Description
Learn how to crack password-based encrypted files.
Summary
In the first part we crack two encrypted files using dictionary attacks with the rockyou wordlist: an encrypted PDF using John directly, and an encrypted ZIP but only after the necessary hash is generated.
For the bonus challenge, we discover an encrypted KeePass Password database, crack its password by first generating the necessary hash with keepass2john and then with John. Inside the database we find a hidden image file which contains the side quest 2 challenge key.
Storyline
Sir Carrotbane discovers encrypted files (North Pole Asset List) on The Best Festival Company’s servers that may contain Santa’s master gift registry. If cracked, Malhare could control the festive balance between worlds. The conflict hinges on whether the Elves can stop the encryption from being breached before their secrets are exposed
Takeaway
Password strength is the primary determinant of encryption security. Weak passwords can be guessed; strong, random ones are far harder to crack.
Security also depends on the algorithm and key derivation method – different formats (PDF, ZIP) use different approaches, affecting vulnerability. Legacy encryption methods remain weak, particularly older ZIP encryption, making these files easier to crack than modern schemes.
Encryption protects confidentiality only and cannot prevent offline password guessing once an attacker has the encrypted file. Ultimately, security hinges on password complexity rather than the encryption technology itself.
Attacks Against Encrypted Files
Theory
Attackers recover weak passwords by guessing them rather than breaking encryption. The two primary methods are dictionary attacks and mask attacks.
Dictionary attacks test passwords from predefined wordlists containing leaked credentials, common substitutions (like ‘password123’), and predictable patterns. This approach is fast and effective because many users choose weak passwords.
Mask attacks are a refined version of brute-force attacks that systematically try character combinations within a specific format (for example, three lowercase letters followed by two digits). This narrows the search space, making the attack faster than trying all possible combinations while remaining more thorough than dictionary attacks alone.
Both techniques exploit human password habits rather than defeating cryptography itself.
Attack Tips
- Simple dictionary attack with wordlists:
rockyou.txtandcommon-passwords.txt - Targeted wordlists: compile company names, project names, and data from the internet
- Mask or incremental attacks on short passwords (for example,
?l?l?l?d?dequals three lowercase letters plus two digits) - Use GPU-accelerated cracking
- Maintain OPSEC: intensive resource use can be detected and monitored
Tools
- PDF:
pdfcrack,johnwith thepdf2johnmodule - ZIP:
fcrackzip,johnwith thezip2johnmodule
Defense Tips
Monitor for the following indicators of password cracking activity: process creation, command patterns, potfiles, GPU artifacts, network activity, and file access.
Cracking binaries: john, hashcat, fcrackzip, pdfcrack, zip2john, pdf2john.pl, 7z, qpdf, unzip, 7za
Command patterns: -w, --wordlist, --rules, --mask, -a 3, -m and references to rockyou.txt or SecLists
Potfiles: ~/.john/john.pot, .hashcat/hashcat.potfile, john.rec
GPU Artifacts: High sustained GPU utilization, long-running HashCat/John processes in nvidia-smi, and loaded GPU libraries (nvcuda.dll, OpenCL.dll, libcuda.so, amdocl64.dll).
Network Activity: Downloads of wordlist files, Git clones of wordlist repos, package installs (apt install john), GPU driver fetches.
File Access: Unusual repeated reads of encrypted or wordlist files.
Process Creation Capture:
- Windows: Sysmon Event ID 1.
ProcessName="C:\Program Files\john\john.exe"
: OR
ProcessName="C:\Tools\hashcat\hashcat.exe"
: OR
CommandLine="*pdf2john.pl*"
: OR
CommandLine="*zip2john*"
- Linux: With
auditdandexecve.
auditctl -w /usr/share/wordlists/rockyou.txt -p r -k wordlists_read
auditctl -a always,exit -F arch=b64 -S execve -F exe=/usr/bin/john -k crack_exec
auditctl -a always,exit -F arch=b64 -S execve -F exe=/usr/bin/hashcat -k crack_exec
Response Playbook
1. Isolate
Remove the affected computer from the network.
2. Collect Evidence
Gather system files – triage artifacts like process lists, process memory dumps, and open files – and encrypted files for investigation. Also, back up the working directory, wordlists, hash files, and shell history.
3. Investigate
Check what was accessed, if data was stolen, and whether the activity was authorized.
4. Respond
If unauthorized, alert the incident response team, change passwords, and enable multi-factor authentication.
5. Improve
Train staff and ensure tools are properly secured to prevent future incidents.
Questions and Answers
Question-1: What is the flag inside the encrypted PDF?
<redacted-flag>
Let us first confirm the file types and then decide on the appropriate cracking software.
ubuntu@tryhackme:~$ ls -hla
...
-rw-r--r--  1 ubuntu ubuntu  42K ... flag.pdf
-rw-r--r--  1 ubuntu ubuntu  245 ... 11:46 flag.zip
drwxrwxr-x 10 ubuntu ubuntu 4.0K ... 15:25 john
...
ubuntu@tryhackme:~$ file flag*
flag.pdf: PDF document, version 1.7, 1 page(s)
flag.zip: Zip archive data, at least v2.0 to extract, compression method=AES Encrypted
ubuntu@tryhackme:~$
We have two target files here: flag.pdf and flag.zip.
We begin with the encrypted PDF file. If we try to open and view the file with atril flag.pdf, we are prompted for a password.
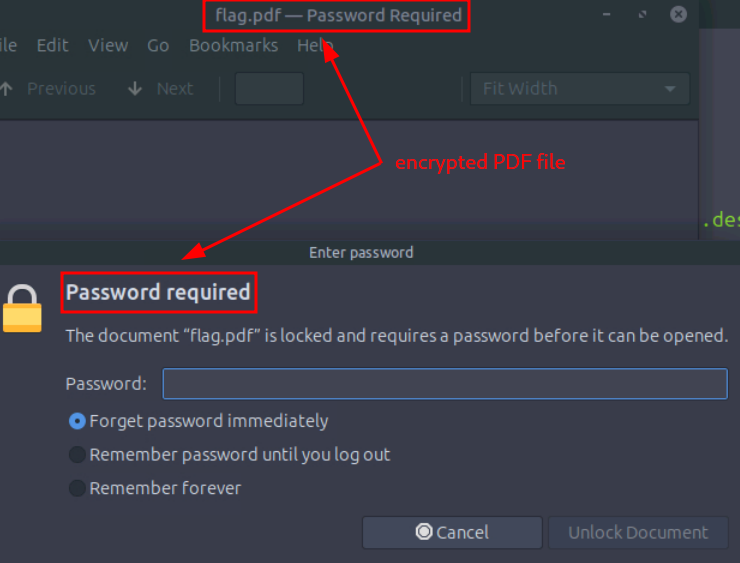
Figure 1: Password prompt when opening the encrypted PDF
Given that it is truly encrypted, we attempt to crack it using a dictionary attack with the rockyou.txt wordlist.
# -f: filename; -w: wordlist
ubuntu@tryhackme:~$ pdfcrack -f flag.pdf -w /usr/share/wordlists/rockyou.txt
PDF version 1.7
Security Handler: Standard
V: 2
R: 3
P: -1060
Length: 128
Encrypted Metadata: True
...
found user-password: <redacted-password>
ubuntu@tryhackme:~$
We use the recovered password to open the PDF file with atril flag.pdf. This reveals the flag for the first question.
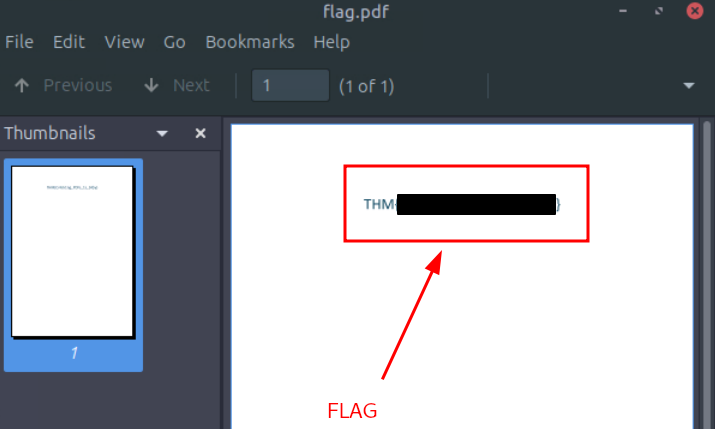
Figure 2: Flag revealed in the decrypted PDF document
Question-2: What is the flag inside the encrypted zip file?
<redacted-flag>
Before proceeding, we verify the target archive.
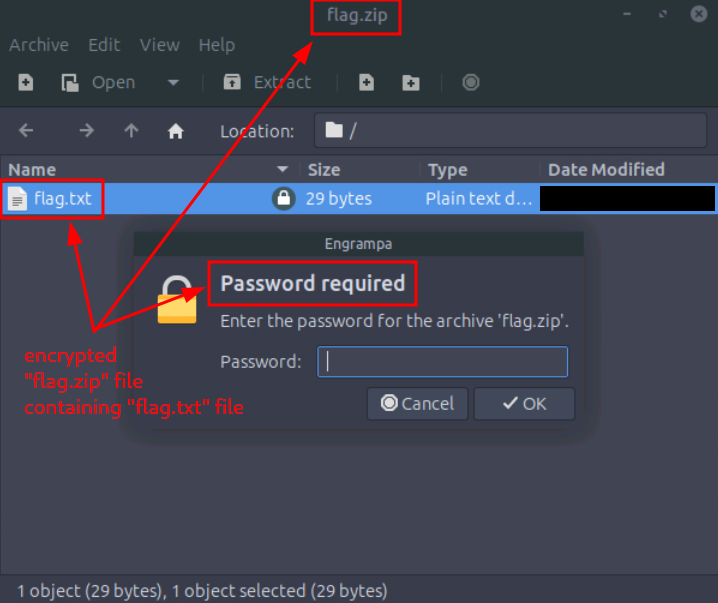
Figure 3: Contents of the encrypted ZIP archive
It contains a flag.txt file, and the archive is truly encrypted, prompting for a password.
For the archive, we first create a hash file – ziphash.txt – with zip2john that we can use with John to crack.
ubuntu@tryhackme:~$ zip2john flag.zip > ziphash.txtWe use the same attack type – dictionary attack – with the same wordlist on the hash.
ubuntu@tryhackme:~$ john --wordlist=/usr/share/wordlists/rockyou.txt ziphash.txt
...
<redacted-password>      (flag.zip/flag.txt)
1g 0:00:00:00 DONE (...) 1.818g/s 7447p/s 7447c/s 7447C/s <redacted-password>
...
ubuntu@tryhackme:~$
The password is recovered quickly; we verify the results.
ubuntu@tryhackme:~$ john ziphash.txt --show
flag.zip/flag.txt:<redacted-password> :flag.txt:flag.zip:flag.zip
...
ubuntu@tryhackme:~$
We open the encrypted archive, decrypt it with the cracked password, and view the flag.
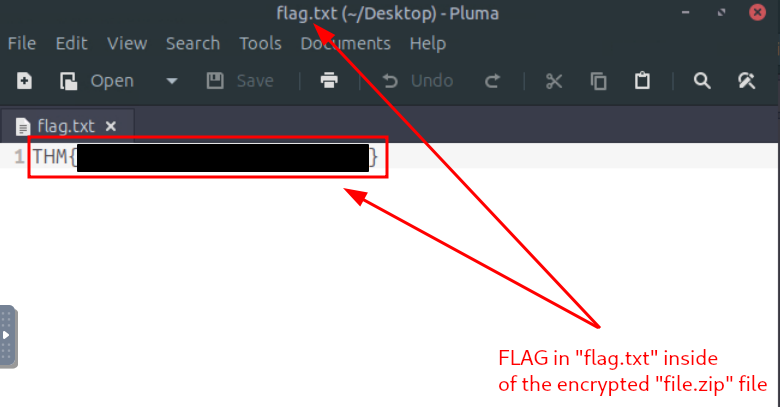
Figure 4: Flag revealed in the decrypted ZIP archive
Side Quest 2 Key Challenge
Bonus-Question-1: For those who want another challenge, have a look around the VM to get access to the key for Side Quest 2! Accessible through our Side Quest Hub!
No answer needed
We examine the current environment to identify any unusual files.
ubuntu@tryhackme:~$ ls -hla
...
-rw-------  1 ubuntu ubuntu 410K ... .Passwords.kdbx
ubuntu@tryhackme:~$
We identify a potential candidate: a KeePass password database named .Passwords.kdbx. We gather more details:
ubuntu@tryhackme:~$ file .Passwords.kdbx
.Passwords.kdbx: Keepass password database 2.x KDBX
ubuntu@tryhackme:~$
To crack it, just as we did with the archive file, we first create a hash file – database.hash – using the keepass2john module from John.
ubuntu@tryhackme:~$ /snap/john-the-ripper/694/bin/keepass2john .Passwords.kdbx > database.hashNow we attempt to crack it using rockyou.txt as the wordlist and KeePass as the format.
ubuntu@tryhackme:~$ john -w /usr/share/wordlists/rockyou.txt --format=KeePass database.hash
...
Loaded 1 password hash (KeePass [AES/Argon2 256/256 AVX2])
...
<redacted-password>     (.Passwords)
1g 0:00:13:53 DONE ([]) 0.001199g/s 2.578p/s 2.578c/s 2.578C/s <redacted-password>
...
Session completed
ubuntu@tryhackme:~$
Although the process takes approximately fifteen minutes, we successfully recover the password. We retrieve it:
ubuntu@tryhackme:~$ john database.hash --show
.Passwords:<redacted-password>
...
ubuntu@tryhackme:~$
and use it to access the KeePass password database with keepassxc .Passwords.kdbx.
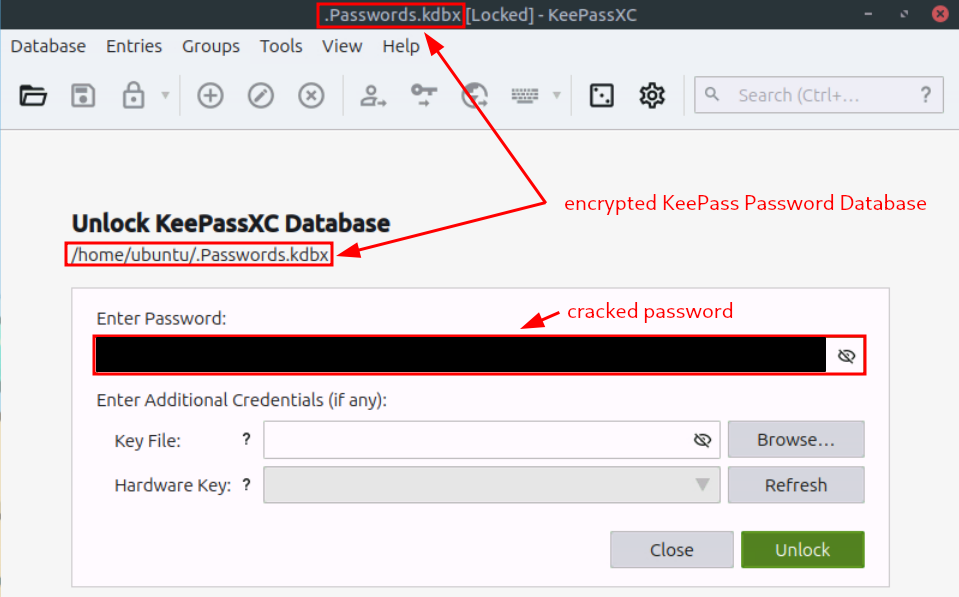
Figure 5: Unlocking the KeePass database with the cracked password
Once the password database is decrypted, only one entry named Key is present inside the database group Root.
The entry appears empty, with no username or password credentials. However, upon checking the Advanced tab, we find an attached image file named sq2.png.
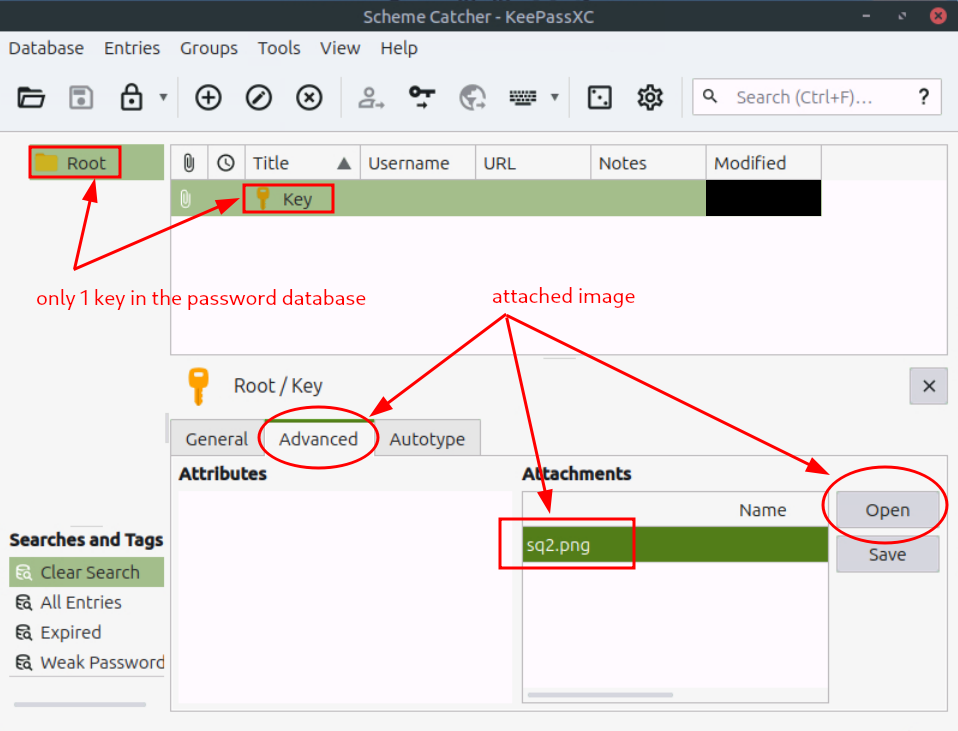
Figure 6: Attached image file in the Advanced tab
Opening the attached image – sq2.png – reveals the hidden key necessary for the Side Quest 2 challenge.
Bonus-Question-2: If you enjoyed this task, feel free to check out the Password Attacks room.
No answer needed