CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 12 Title: Phishing - Phishmas Greetings |
Description
Learn how to spot phishing emails from Malhare’s Eggsploit Bunnies sent to TBFC users.
Summary
Here we move on to inspect some emails in order to identify various phishing attempts. Some of these make use of email address spoofing techniques, others use falsely advertised – potentially malicious – attachment files. There are also some others that use typosquatting/punycode, but most default to some basic social engineering techniques.
Storyline
McSkidy’s disappearance has disabled TBFC’s email filters. The SOC Team suspects Malhare’s Eggsploit Bunnies launched a phishing campaign to steal credentials. You must identify legitimate emails versus sophisticated phishing attempts disguised as routine operations or SOC-mas logistics.
Spotting Phishing Emails
Phishing is a precision-targeted cyber attack exploiting human vulnerability to steal credentials, deliver malware, exfiltrate data, or commit financial fraud.
It remains highly effective because it targets people, not technology.
Phishing vs. Spam
Phishing is deliberate deception targeting specific users. Spam is bulk, low-risk marketing noise with goals to push exposure or engagement.
Its intentions include: promotion, scams, traffic generation (clickbait), and data harvesting. The best defense is to look for the intention behind it.
Core Techniques
Impersonation
Attackers pose as trusted individuals or departments using mismatched domains (e.g., Gmail instead of company domain). The best defense against it: check if the sender’s email matches the expected domain.
Social Engineering
This technique manipulates emotions through urgency, fear, or trust; often redirects victims away from official verification channels (side channel). Some of the common techniques include: impersonation, sense of urgency, side channel, and malicious intention.
Typosquatting
Typosquatting registers misspelled domains (glthub.com vs. github.com).
Punycode
Punycode replaces ASCII letters with visually identical Unicode characters (Latin a becomes Greek α). The best defense against it is to check the email headers’ Return-Path field for ACE prefix encoding.
Spoofing
Messages appear legitimate (display name and From:) but fail authentication checks (SPF, DKIM, DMARC). Failed SPF and DMARC indicate spoofing.
The best defense against it is to check the Headers > Authentication-Results (spf=fail; dkim=fail; dmarc=fail). Also, check the Return-Path.
- SPF: Says which servers are allowed to send emails for a domain (like a list of approved senders)
- DKIM: Adds a digital signature to prove the message was not changed and really came from that domain
- DMARC: Uses SPF and DKIM to decide what to do if something looks fake (for example, send it to spam or block it)
Malicious Attachments
Attaching malicious files to an email usually uses some sort of social engineering technique in the body. Common types include .html and .hta files because they execute without browser sandboxing, providing full endpoint access.
Modern Tactics
Attackers now focus on stealing credentials rather than dropping malware. They exploit legitimate applications (Google Drive, OneDrive, Dropbox) to bypass filters, create fake login pages (microsoftonline.login444123.com/signin) mimicking Office 365/Google, and use side-channel communications (SMS, WhatsApp, phone calls) to escape company security controls.
Defense
User awareness is critical. Verify sender domains, check authentication headers, recognize social engineering, and question requests creating artificial urgency.
Questions and Answers
First, we start the target VM and then open the web application.
It seems that the Automatic classification function is disabled, so we have to inspect the emails manually. There are six emails in our inbox.
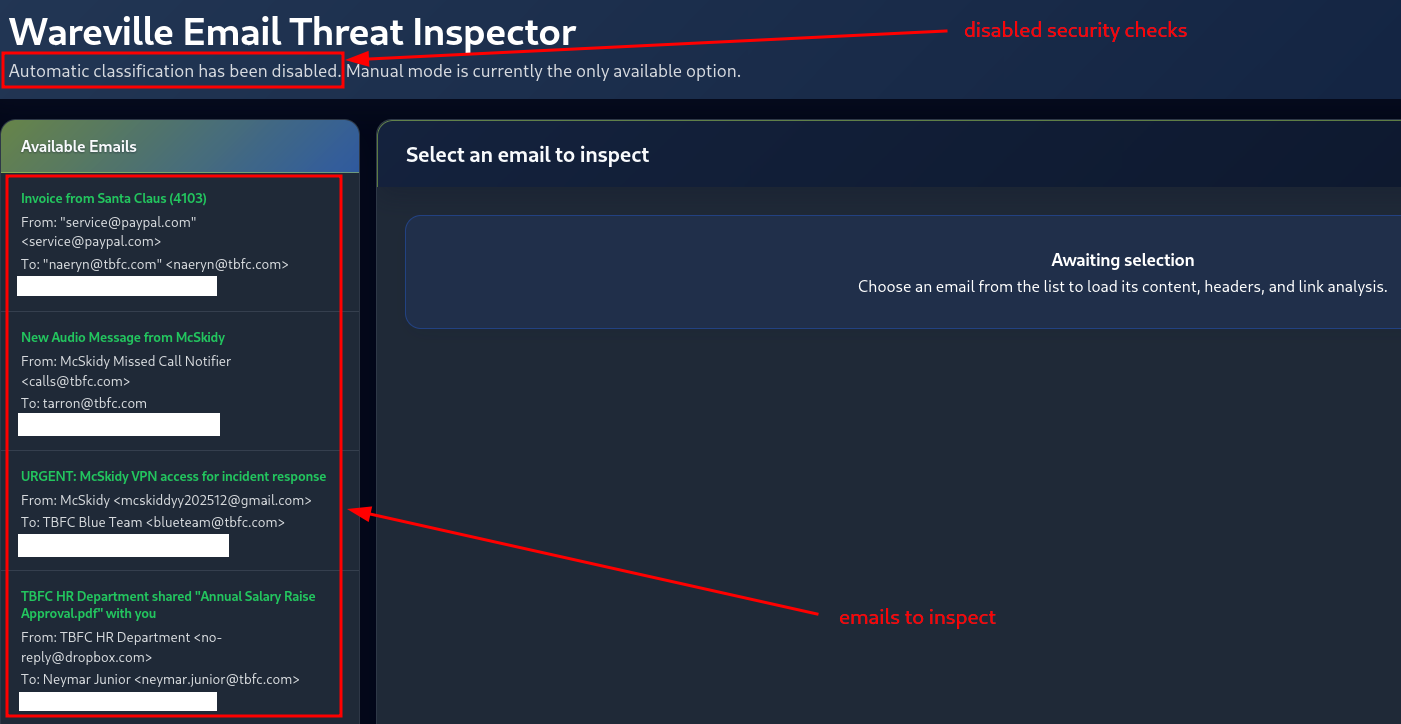
Figure 1: Email inbox with six messages awaiting classification
We begin with the first one by clicking on it under Available Emails.
Figure 2: First email selected for inspection
Question-1: Classify the 1st email, what’s the flag?
<redacted-flag>
It looks like we have an Email Spoofing Attempt here. There are several indicators we can examine to verify it.
First, under Headers, we can check the AUTHENTICATION-RESULTS email header.
The fact that all authentication checks – SPF, DKIM, and DMARC – report failures is a strong indicator of a spoofing attempt.
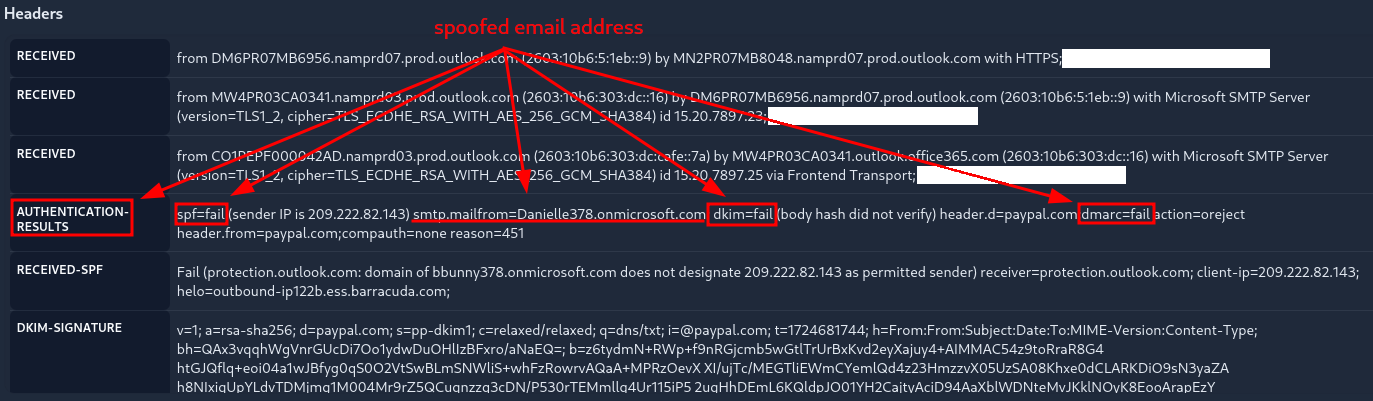
Figure 3: First email with failed SPF, DKIM, and DMARC authentication checks
Moreover, when we check the RETURN-PATH header, we notice a mismatch between the sender, the advertised, and the real return email address.
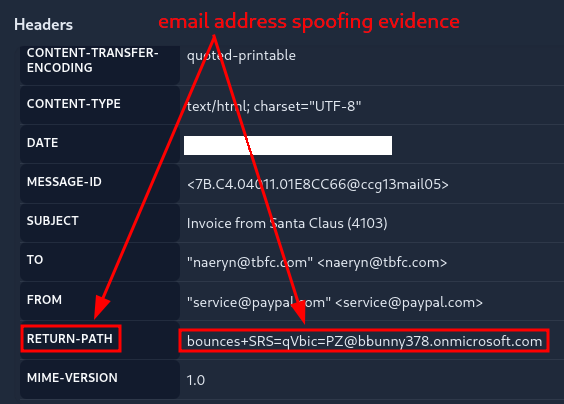
Figure 4: First email showing Return-Path header mismatch
Once we identify the issue, we classify the email.
When we submit the correct classification, we receive the flag for the first question.
CLASSIFICATION: Phishing – Spoofing, Sense of Urgency, Fake Invoice
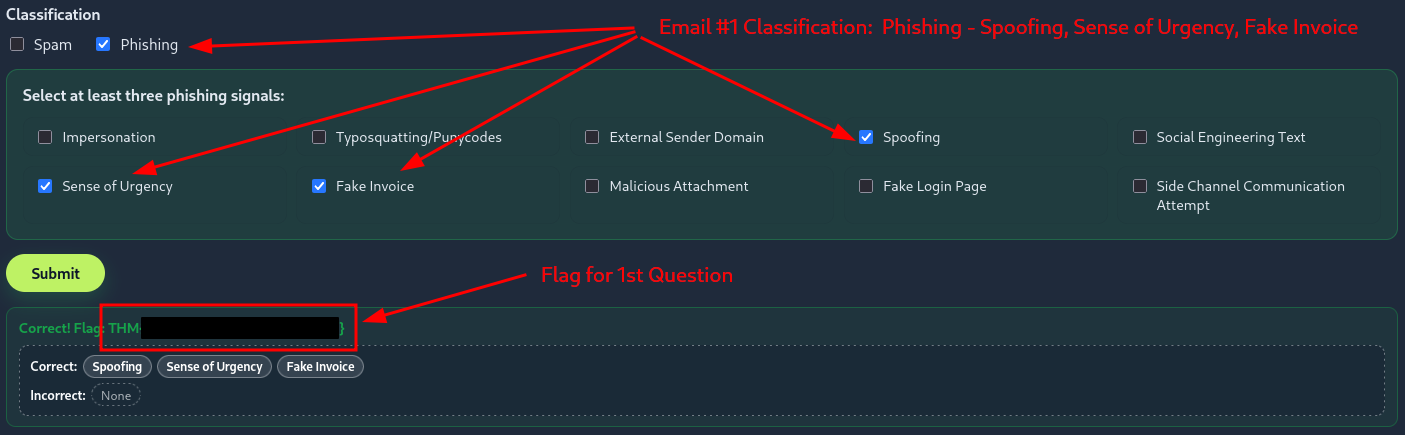
Figure 5: First email classification result displaying the flag
Question-2: Classify the 2nd email. What’s the flag?
<redacted-flag>
Here we notice a potentially malicious attachment file, which is advertised as an MP3 file when in fact it is an HTML file.
Moreover, just like before, there is an issue with both the Authentication-Results and the Return-Path header.
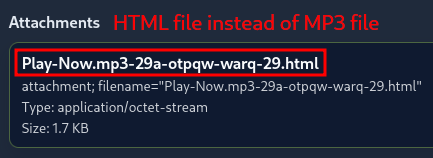
Figure 6: Second email with disguised malicious attachment
Indicators
- AUTHENTICATION-RESULTS Header:
spf=fail;dkim=fail;dmarc=fail - RETURN-PATH Header:
[email protected]instead of[email protected] - Attachments: HTML file –
Play-Now.mp3-29a-otpqw-warq-29.html– instead of MP3 file
CLASSIFICATION: Phishing – Impersonation, Spoofing, Malicious Attachment
Question-3: Classify the 3rd email. What’s the flag?
<redacted-flag>
Indicators
- Sense of urgency text: Contains ‘immediately’, ‘urgent’
- Side channel communication attempt: Attempts to redirect communication to “personal email”
CLASSIFICATION: Phishing – Impersonation, Social Engineering Text, Sense of Urgency
Question-4: Classify the 4th email. What’s the flag?
<redacted-flag>
Here we notice a domain mismatch in the body of the email.
The account that shares the document with us via Dropbox is [email protected] of the OUTLOOK.COM domain, instead of our company domain which is TBFC.COM.
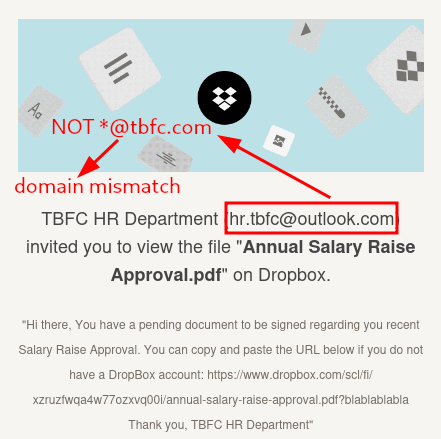
Figure 7: Fourth email displaying external domain mismatch in Dropbox sharing request
Indicators: Domain Mismatch
CLASSIFICATION: Phishing – Impersonation, External Sender Domain, Social Engineering Text
Question-5: Classify the 5th email. What’s the flag?
<redacted-flag>
Indicators
- Authentication Results headers pass
- Return-Path header matches with sender
- No attachment and no links
CLASSIFICATION: Spam
Question-6: Classify the 6th email. What’s the flag?
<redacted-flag>
Here we notice a Punycode attempt with the ASCII letter “f”.
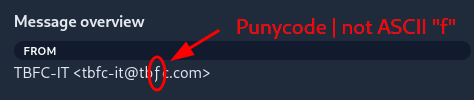
Figure 8: Sixth email displaying Punycode character substitution in sender address
For the real – correct ASCII encoded sender address – we check the Return-Path header which identifies it as [email protected] instead of [email protected].
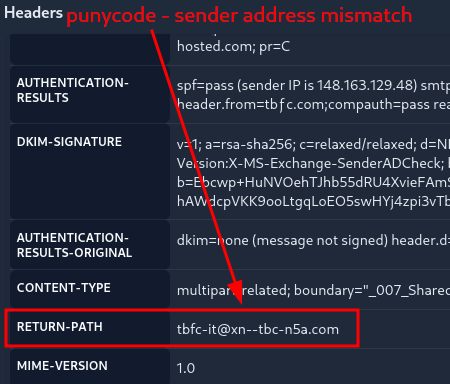
Figure 9: Sixth email Return-Path header showing true Punycode domain
Indicators
- Punycode in sender email address
ƒinstead of ASCIIf - Return-Path Header:
[email protected]instead of[email protected]
CLASSIFICATION: Phishing – Impersonation, Typosquatting/Punycode, Social Engineering Text
Question-7: If you enjoyed today’s room, you can explore the Phishing Analysis Tools room in detail!
No answer needed