CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 15 Title: Web Attack Forensics - Drone Alone |
Description
Explore web attack forensics using Splunk.
Summary
Day 15 is about analyzing a web server compromise in Splunk by examining multiple log sources to trace an attack from initial access to post-exploitation activity. We first search web access logs and find Base64-encoded PowerShell payloads targeting a vulnerable CGI script. Decoding it reveals a gloating message, confirming successful exploitation.
We then check Apache error logs to determine if attacks reached the backend or were blocked at the web layer. Next, we examine Sysmon process logs and discover child processes spawned by Apache, proving successful command injection at the OS level.
Lastly, we identify post-exploitation reconnaissance commands, showing the attacker probing their privilege level. Finally, we search for encoded PowerShell commands in Sysmon logs and find none, indicating defenses successfully blocked further encoded payload execution.
Storyline
TBFC’s drone scheduler web UI is compromised by Base64-encoded malicious payloads in HTTP requests that trigger remote code execution on vulnerable endpoints. Splunk detected Apache spawning suspicious processes, revealing obfuscated shell code hidden within the payloads.
Preparation
Open the Splunk Enterprise web interface by visiting the provided link after starting the target VM. Be aware that it might take a while for the setup to be ready (~5+ min).
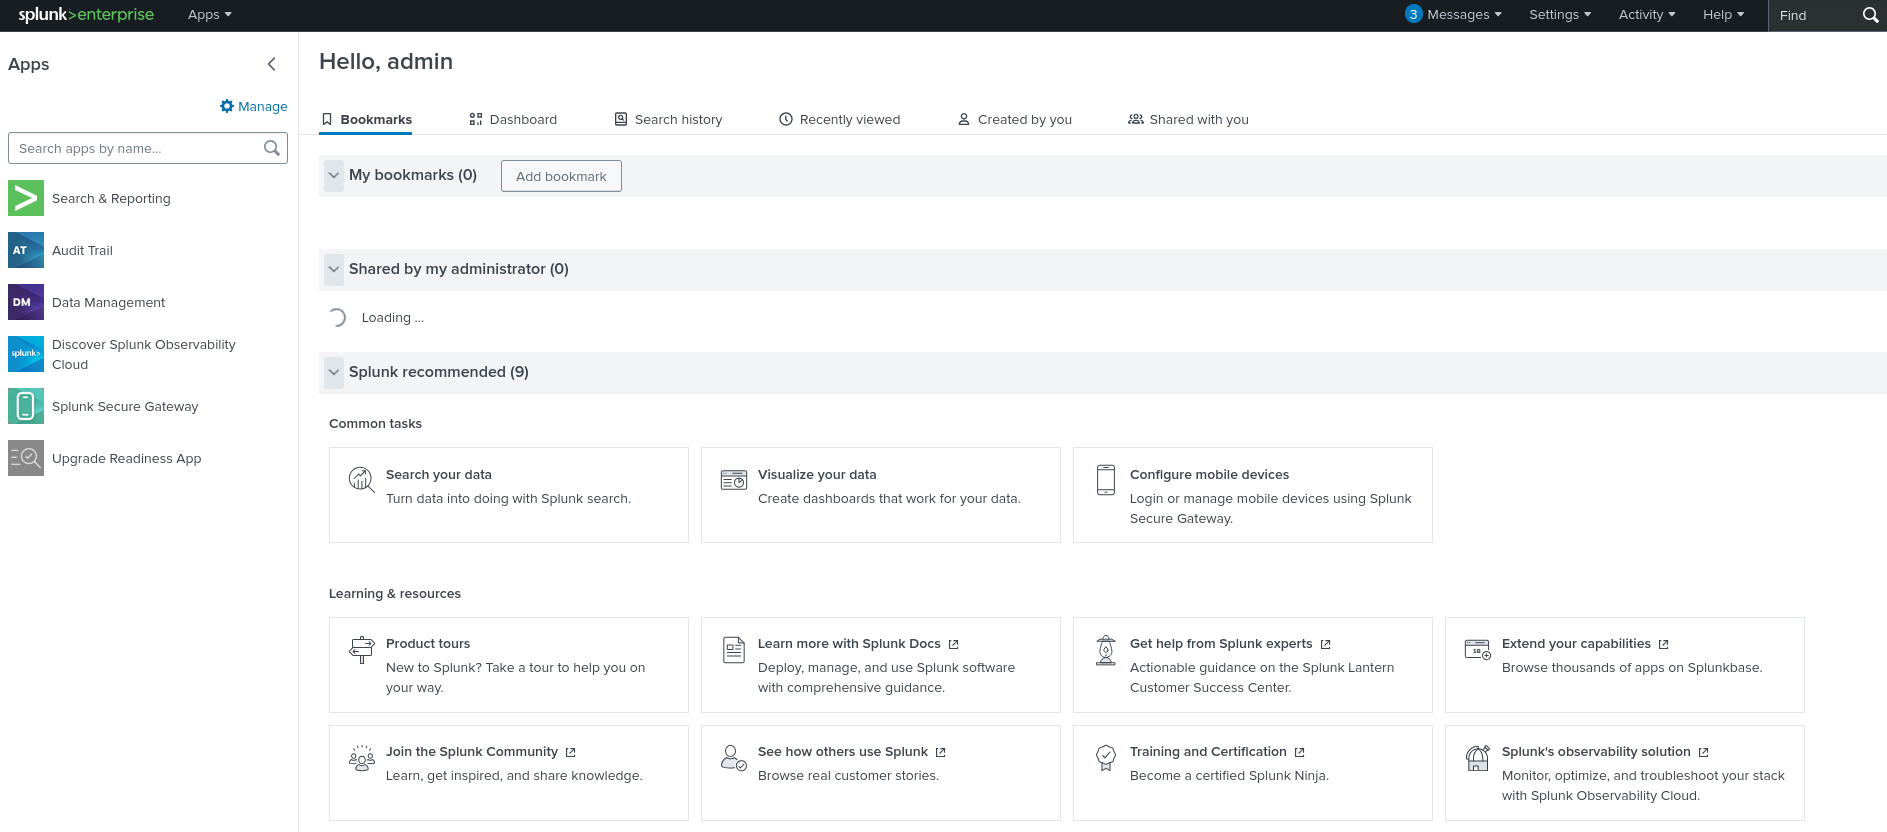
Figure 1: Splunk Enterprise login screen
Once the web interface loads, navigate to Search & Reporting.
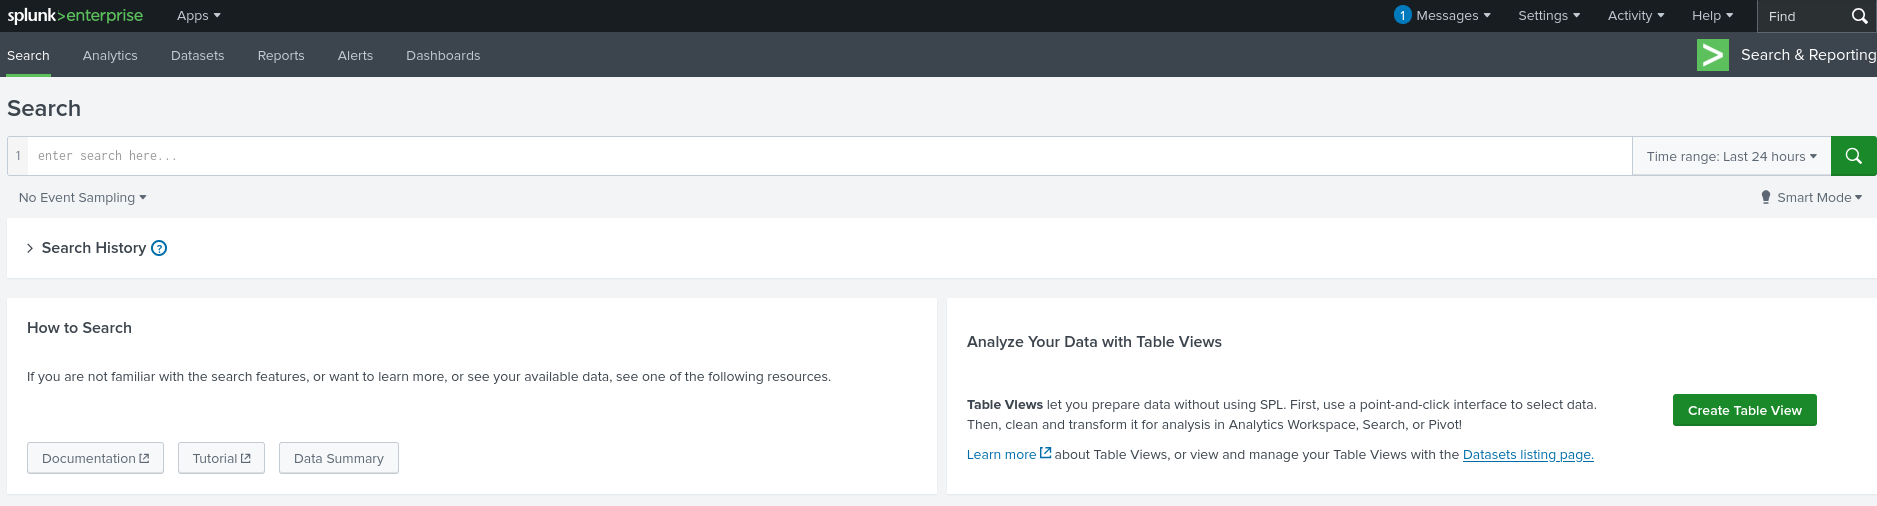
Figure 2: Splunk Enterprise home dashboard with Search & Reporting option
Adjust the Time range for searches to include all reported events by selecting All time.
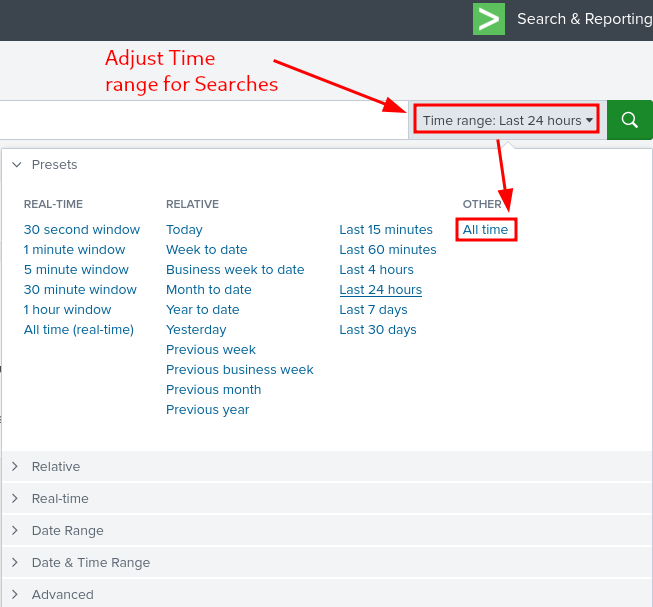
Figure 3: Adjusting the search time range to All time
Web Logs
Web Access Logs
Search web access logs for HTTP requests containing signs of command execution attempts such as cmd.exe, PowerShell, Invoke-Expression, and possible command injection attacks where system command execution is performed through a vulnerable CGI script – hello.bat:
index=windows_apache_access (cmd.exe OR powershell OR "powershell.exe" OR "Invoke-Expression") | table _time host clientip uri_path uri_query status
Upon closer inspection of the reported events, we notice suspicious Base64-encoded PowerShell payloads in the uri_query field.
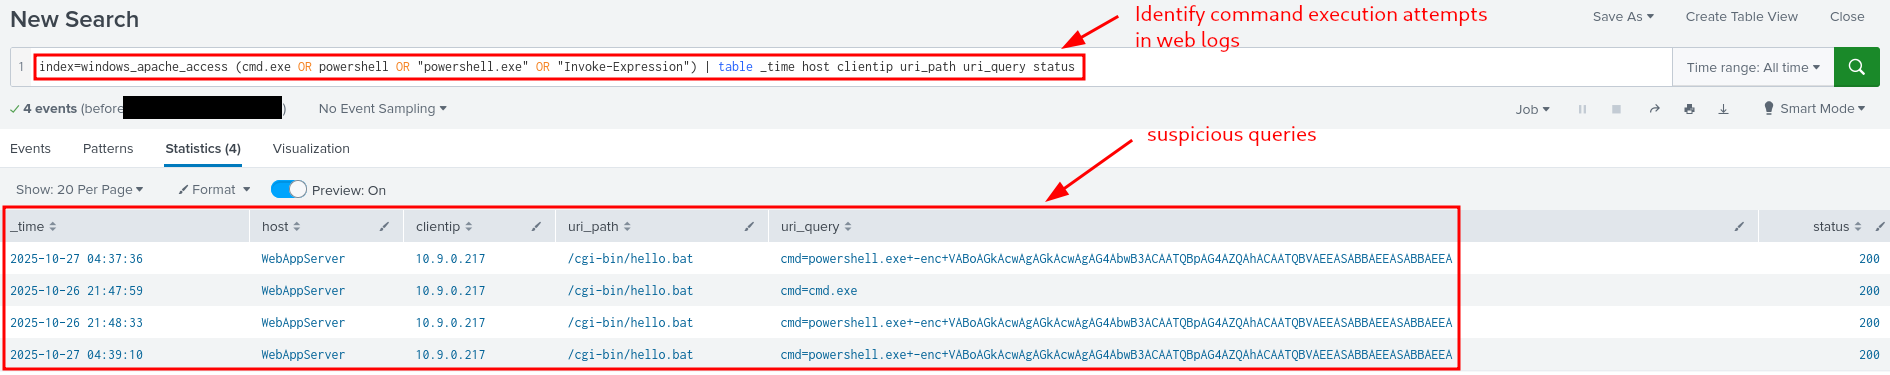
Figure 4: Detecting command execution attempts in web access logs
The same payload was attempted three times: VABoAGkAcwAgAGkAcwAgAG4AbwB3ACAATQBpAG4AZQAhACAATQBVAEEASABBAEEASABBAEEA.
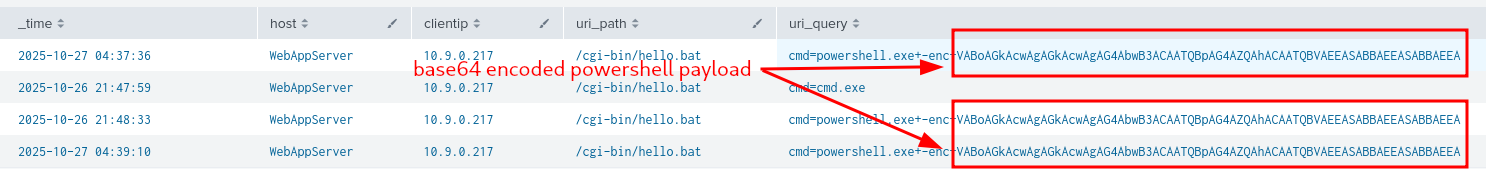
Figure 5: Base64-encoded PowerShell payload in the URI query string
We decode the payload by switching to our attacker Kali machine and using the -d (decode) option with base64:
user@kali:~$ echo -n "VABoAGkAcwAgAGkAcwAgAG4AbwB3ACAATQBpAG4AZQAhACAATQBVAEEASABBAEEASABBAEEA" | base64 -d
This is now Mine! MUAHAAHAA
user@kali:~$
The decoded results reveal a gloating message – “This is now Mine! MUAHAAHAA” – indicating that an attacker likely achieved some level of success penetrating the system.
Additional interesting data accompanies the encoded payload:
- Time Range: 2025-10-26 21:47:59 – 2025-10-27 04:39:10
- Host: WebAppServer
- Client IP: 10.9.0.217
- URI Path:
/cgi-bin/hello.bat - Response Status Codes: all 200
Web Error Logs
We examine Apache error logs for server-side errors or command execution indicators, looking for signs of execution attempts or internal failures caused by malicious requests.
Query:
index=windows_apache_error ("cmd.exe" OR "powershell" OR "Internal Server Error")
Query results:
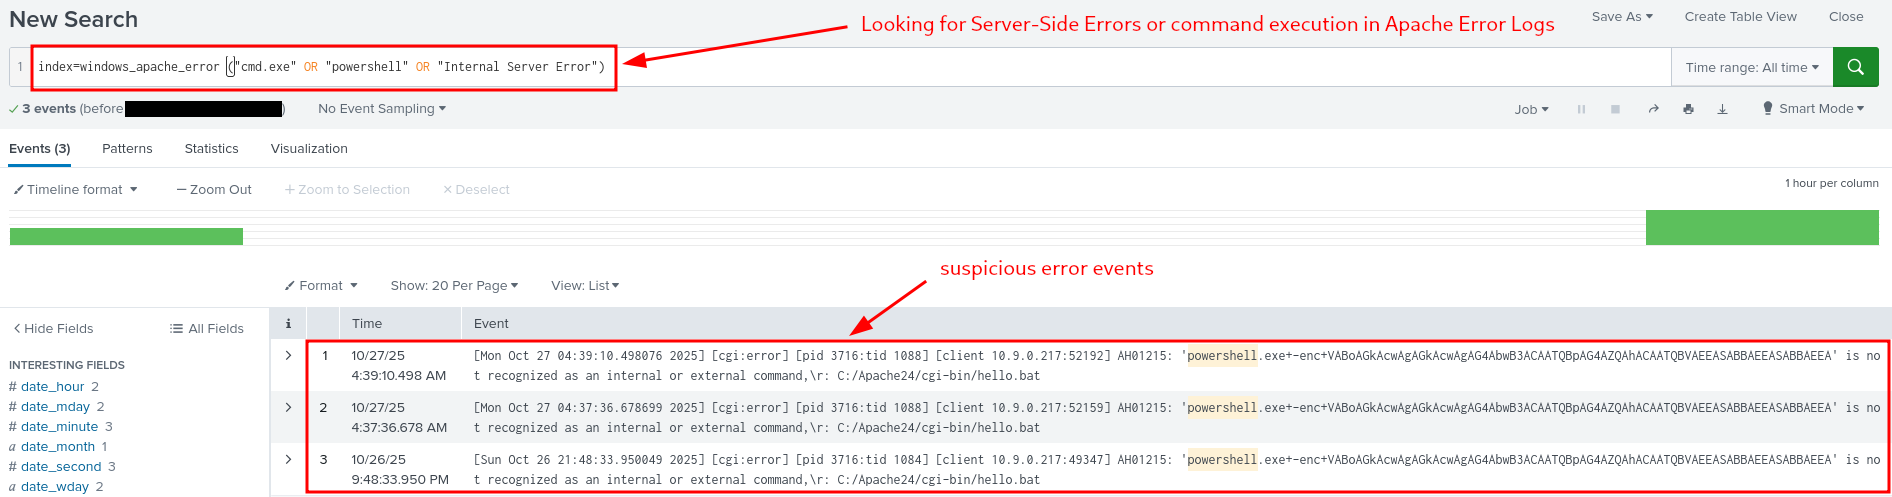
Figure 6: Failed command execution attempts in Apache error logs
Select Raw View instead of the default List View by clicking View: List and selecting Raw from the dropdown menu.
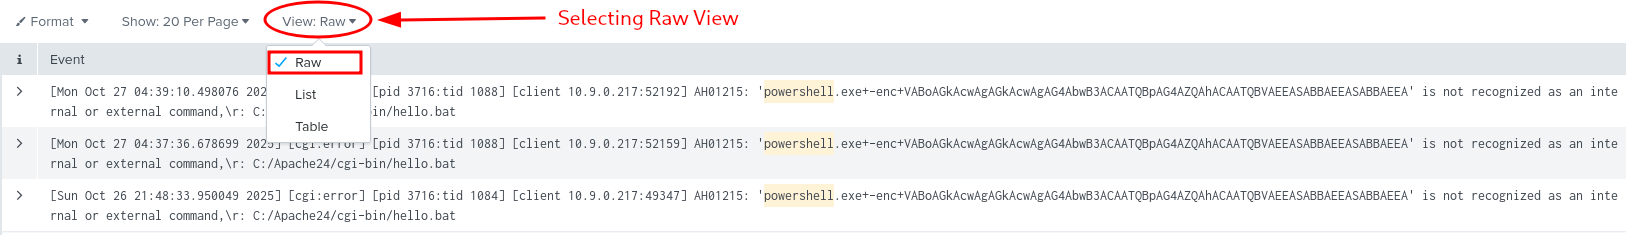
Figure 7: Selecting Raw View for improved readability
The rationale for checking error logs is that some exploit attempts fail or get blocked.
For example, a request to /cgi-bin/hello.bat?cmd=powershell triggering a “500 Internal Server Error” could indicate that the attacker’s input was processed by the server but failed during execution, which would indicate a clear exploitation attempt.
Simply put, checking error logs helps confirm whether an attack reached the backend or remained blocked at the web layer.
Sysmon Data
Command Injection Attempts
We check Sysmon logs for processes spawned by httpd.exe – the web server:
index=windows_sysmon ParentImage="*httpd.exe"
There are fourteen entries here. We change our view from List to Table to get a better picture of the activity.
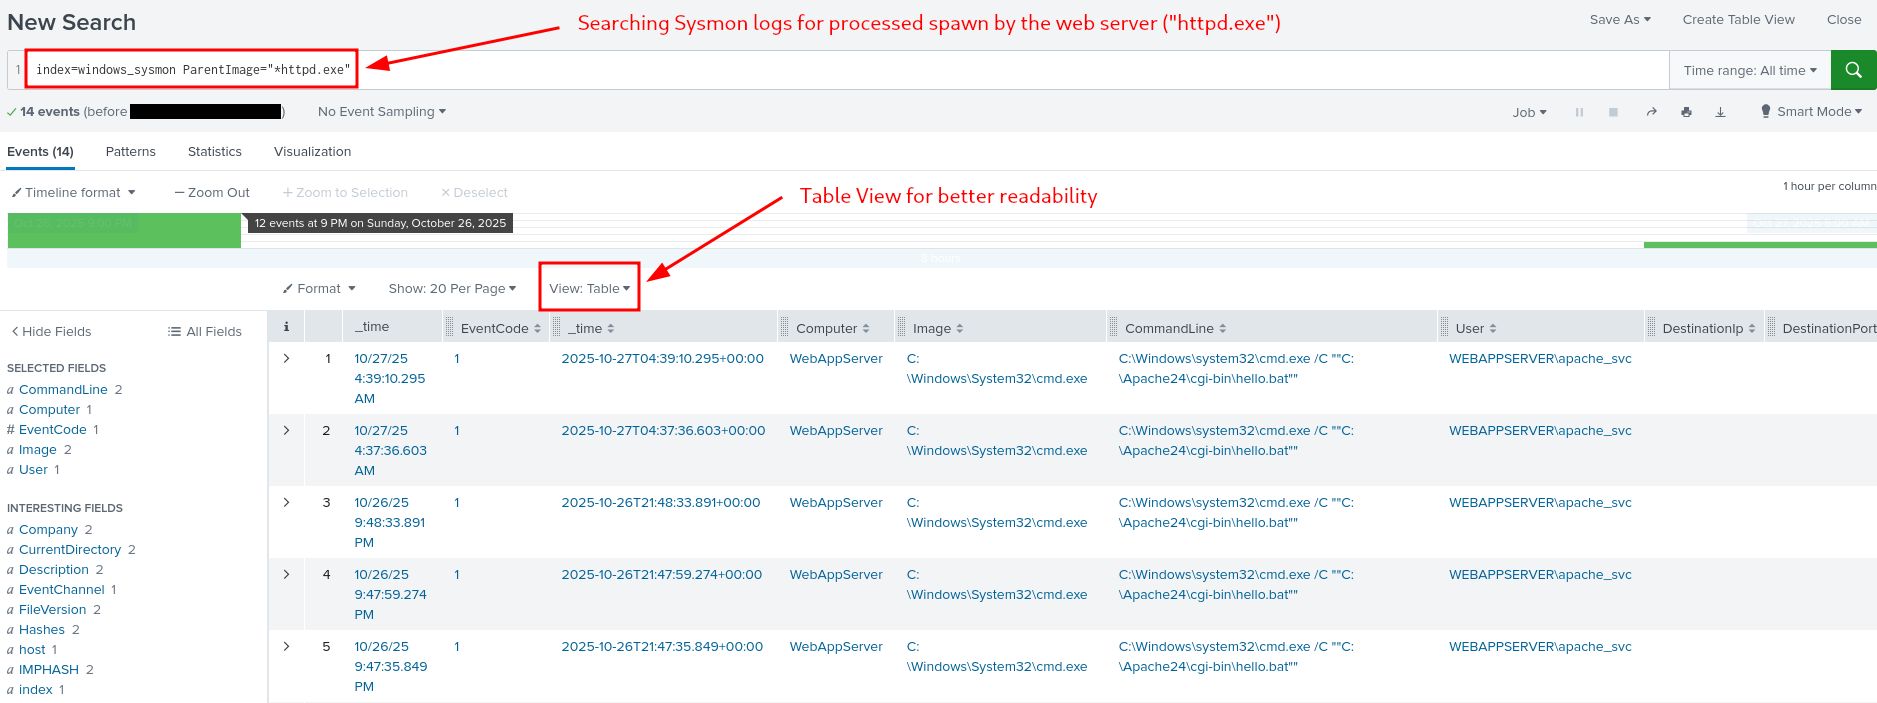
Figure 8: Processes spawned by the Apache web server
To understand these results, note that the Apache process should only spawn worker threads, not system processes such as cmd.exe or powershell.exe.
Therefore, any results showing child processes such as Image = C:\Windows\System32\cmd.exe with Apache as the parent process – ParentImage = C:\Apache24\bin\httpd.exe – indicates successful command injection, where a system command was executed by Apache.
In summary, this finding indicates that the web attack penetrated the operating system.
Enumerating Suspicious Activity
We search for indicators of post-exploitation reconnaissance, such as the attacker running whoami in CMD to determine which user account their malicious process is running as.
Query:
index=windows_sysmon *cmd.exe* *whoami*
Query result:
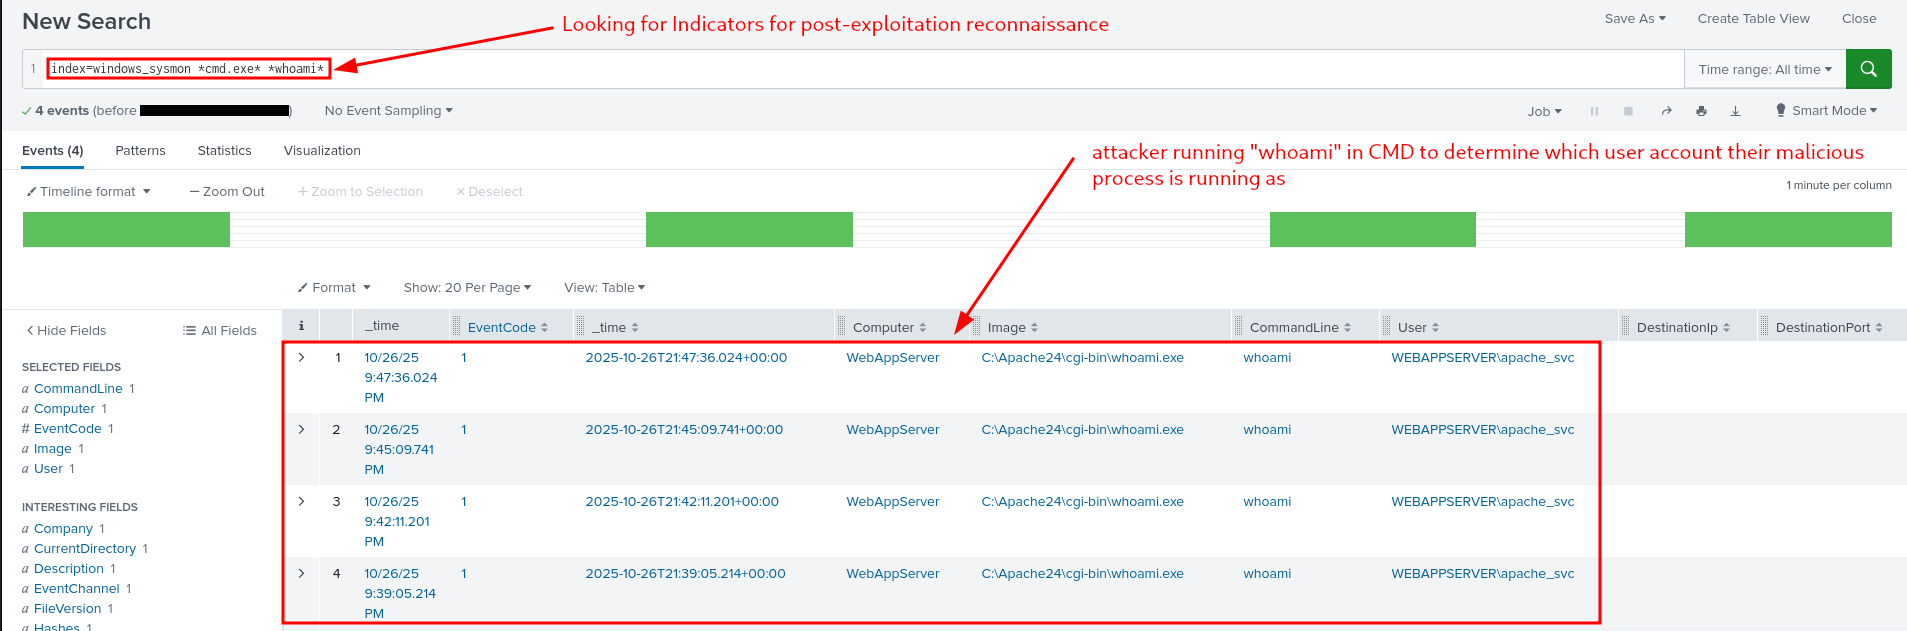
Figure 9: Post-exploitation reconnaissance activity
Encoded Payloads
We search for encoded strings or commands successfully run by PowerShell within Sysmon data:
index=windows_sysmon Image="*powershell.exe" (CommandLine="*enc*" OR CommandLine="*-EncodedCommand*" OR CommandLine="*Base64*")
The rationale: if defenses were adequate, such execution was blocked and nothing appears in the results.
If, on the other hand, results appear, we can determine when and exactly what was run, providing insight into the attacker’s intentions.
Fortunately, nothing appears here, meaning that our defenses were sufficient today.
Questions and Answers
Question-1: What is the reconnaissance executable file name?
whoami.exe
Question-2: What executable did the attacker attempt to run through the command injection?
PowerShell.exe