CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 16 Title: Forensics - Registry Forensics |
Description
Learn what the Windows Registry is and how to investigate it.
Summary
Here we investigate a compromised system using Registry Explorer to analyze offline registry hives. We start by loading the registry hives from dispatch-srv01 and navigate through key forensic locations. We check the SOFTWARE hive’s Uninstall keys and identify that DroneManager Updater was installed before the abnormal activity began.
We then examine the UserAssist registry and find where the user launched the malicious installer from. Finally, we check the Run registry key and discover the persistence mechanism that the attacker configured to maintain startup access.
Storyline
TBFC is under attack. McSkidy’s well-trained team is conducting forensic analysis on dispatch-srv01, a critical drone-delivery system compromised by attackers. The team is splitting into specialized groups to investigate logs, memory dumps, file systems, and registry data – our focus is the registry analysis.
Theory
Overview and Core Function
The Windows Registry is the operating system’s configuration database, functioning as the brain of Windows by storing all essential system and user information needed for proper OS operation.
Unlike the human brain’s single physical location, the Registry is distributed across multiple separate files called Hives, each storing different categories of configuration data.
Registry Hives
SYSTEM
- Services, mounted devices, boot configuration, drivers, hardware settings
- C:\Windows\System32\config\SYSTEM
SECURITY
- Local security policies, audit policy settings
- C:\Windows\System32\config\SECURITY
SOFTWARE
- Installed programs, OS version info, autostarts, program settings
- C:\Windows\System32\config\SOFTWARE
SAM
- Usernames, password hashes, group memberships, account statuses
- C:\Windows\System32\config\SAM
NTUSER.DAT
- Recent files, user preferences, user-specific autostarts
- C:\Users\username\NTUSER.DAT
USRCLASS.DAT
- Shellbags, jump lists
- C:\Users\username\AppData\Local\Microsoft\Windows\USRCLASS.DAT
Registry Root Keys
Windows organizes Registry Hives into structured Root Keys displayed in the Registry Editor. The mapping between hives and root keys is as follows:
SYSTEM
- HKEY_LOCAL_MACHINE\SYSTEM
- HKLM\SYSTEM
SECURITY
- HKEY_LOCAL_MACHINE\SECURITY
- HKLM\SECURITY
SOFTWARE
- HKEY_LOCAL_MACHINE\SOFTWARE
- HKLM\SOFTWARE
SAM
- HKEY_LOCAL_MACHINE\SAM
- HKLM\SAM
NTUSER.DAT
- HKEY_USERS\<SID> and HKEY_CURRENT_USER
- HKU\<SID> and HKCU
USRCLASS.DAT
- HKEY_USERS\<SID>\Software\Classes
- HKU\<SID>\Software\Classes
Key organizational points:
HKLM (HKEY_LOCAL_MACHINE)
- Contains most system-wide hives: SYSTEM, SOFTWARE, SECURITY, SAM.
HKU/HKCU (HKEY_USERS/HKEY_CURRENT_USER)
- Contain user-specific hives: NTUSER.DAT, USRCLASS.DAT.
HKCR/HKCC (HKEY_CLASSES_ROOT/HKEY_CURRENT_CONFIG)
- Are dynamically populated during Windows runtime and are not backed by separate hive files.
Accessing Registry Data
Registry Hives contain binary data and cannot be opened directly by double-clicking their files.
Windows provides the built-in Registry Editor tool (accessible via the search bar) to view registry data in a human-readable hierarchical format organized by root keys and subkeys.
Navigation Example: Connected USB Devices
- Navigate to
HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Enum\USBSTOR. - Displays: USB device information including make, model, device ID, manufacturer identification, and unique device identifiers
Navigation Example: User-Run Programs
- Navigate to
HKEY_CURRENT_USER\Software\Microsoft\Windows\CurrentVersion\Explorer\RunMRU - Displays: Commands executed via the Win+R Run dialog.
Registry Forensics
Registry forensics is the process of extracting and analyzing evidence from the Registry for Windows digital forensic investigations, where analysts examine registry data alongside event logs, file system data, and memory data to construct incident timelines.
Key Forensic Registry Locations
Recently accessed GUI-launched applications
- HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\UserAssist
Paths and locations typed in Explorer address bar
- HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\TypedPaths
Application file paths
- HKLM\Software\Microsoft\Windows\CurrentVersion\App
Search terms entered in Explorer search bar
- HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\WordWheelQuery
Startup programs configured for automatic launch
- HKLM\Software\Microsoft\Windows\CurrentVersion\Run
Recently accessed files
- HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\RecentDocs
Computer hostname
- HKLM\SYSTEM\CurrentControlSet\Control\ComputerName\ComputerName
Installed programs inventory
- HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Uninstall
Registry Editor limitations
- Cannot open offline hives (required for forensic analysis to prevent system modification)
- Displays some key values in unreadable binary format
Specialized registry forensics tools – such as Registry Explorer – parse binary data and enable offline analysis without risk of modifying the original system evidence.
Dirty Hives
Registry Hives that were collected from live systems and may have incomplete transactions.
Use clean loading on them: Registry Explorer > File > Load hive > Load Hives pop-up > Select desired hive file > hold SHIFT then press Open.
Practical
- Tool: Registry Explorer
- Hives:
C:\Users\Administrator\Desktop\Registry Hives - Investigated Host: dispatch-srv01
- Time Range: from 2025.11.21 on
Preparation
Start the target VM, open Registry Explorer, and load the registry hives for dispatch-srv01 by:
Registry Explorer > File tab > Load hive > Select all files in C:\Users\Administrator\Desktop\Registry Hives\ > Press SHIFT and Open.
Questions and Answers
Question-1: What application was installed on the dispatch-srv01 before the abnormal activity started?
DroneManager Updater
Head over to Available bookmarks, under the loaded SOFTWARE hive entries – C:\Users\Administrator\Desktop\Registry Hives\SOFTWARE – and select Uninstall.
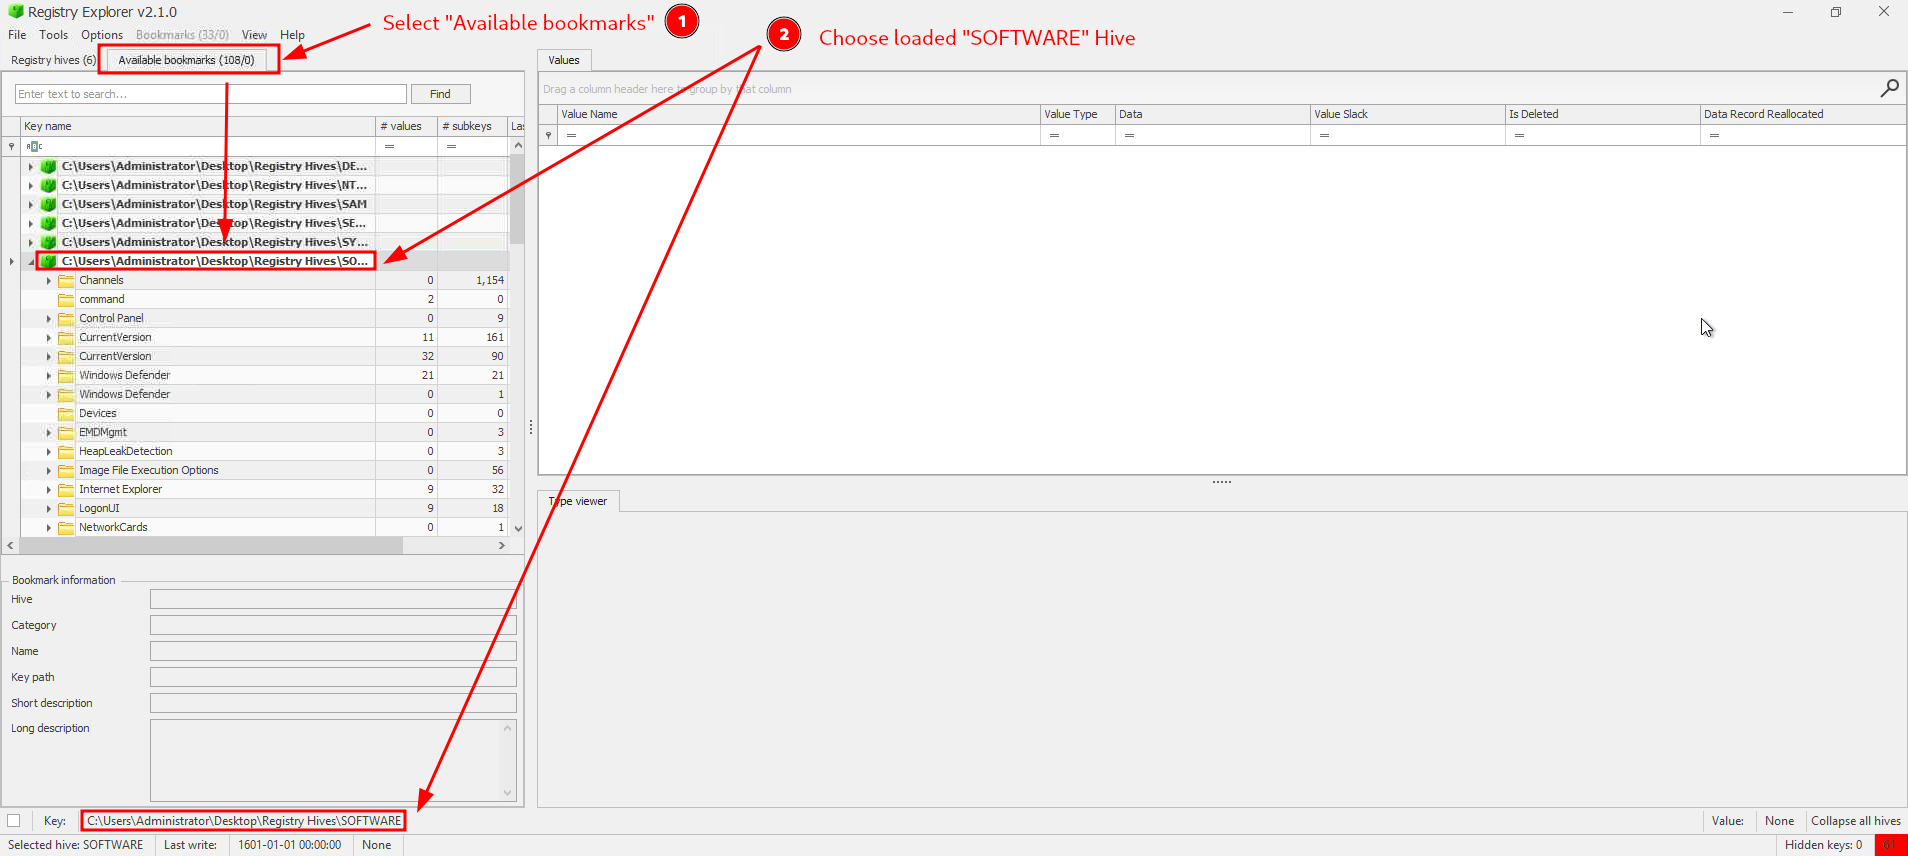
Figure 1: Registry Explorer showing the SOFTWARE hive selected from Available bookmarks
Note that there are two Uninstall keys:
- one with the last timestamp entry on 2025-10-20 20:16:40 with Microsoft EdgeWebView, and another
- with the timestamp entry of 2025-10-21 20:52:37 by DroneManager Updater (64bit).
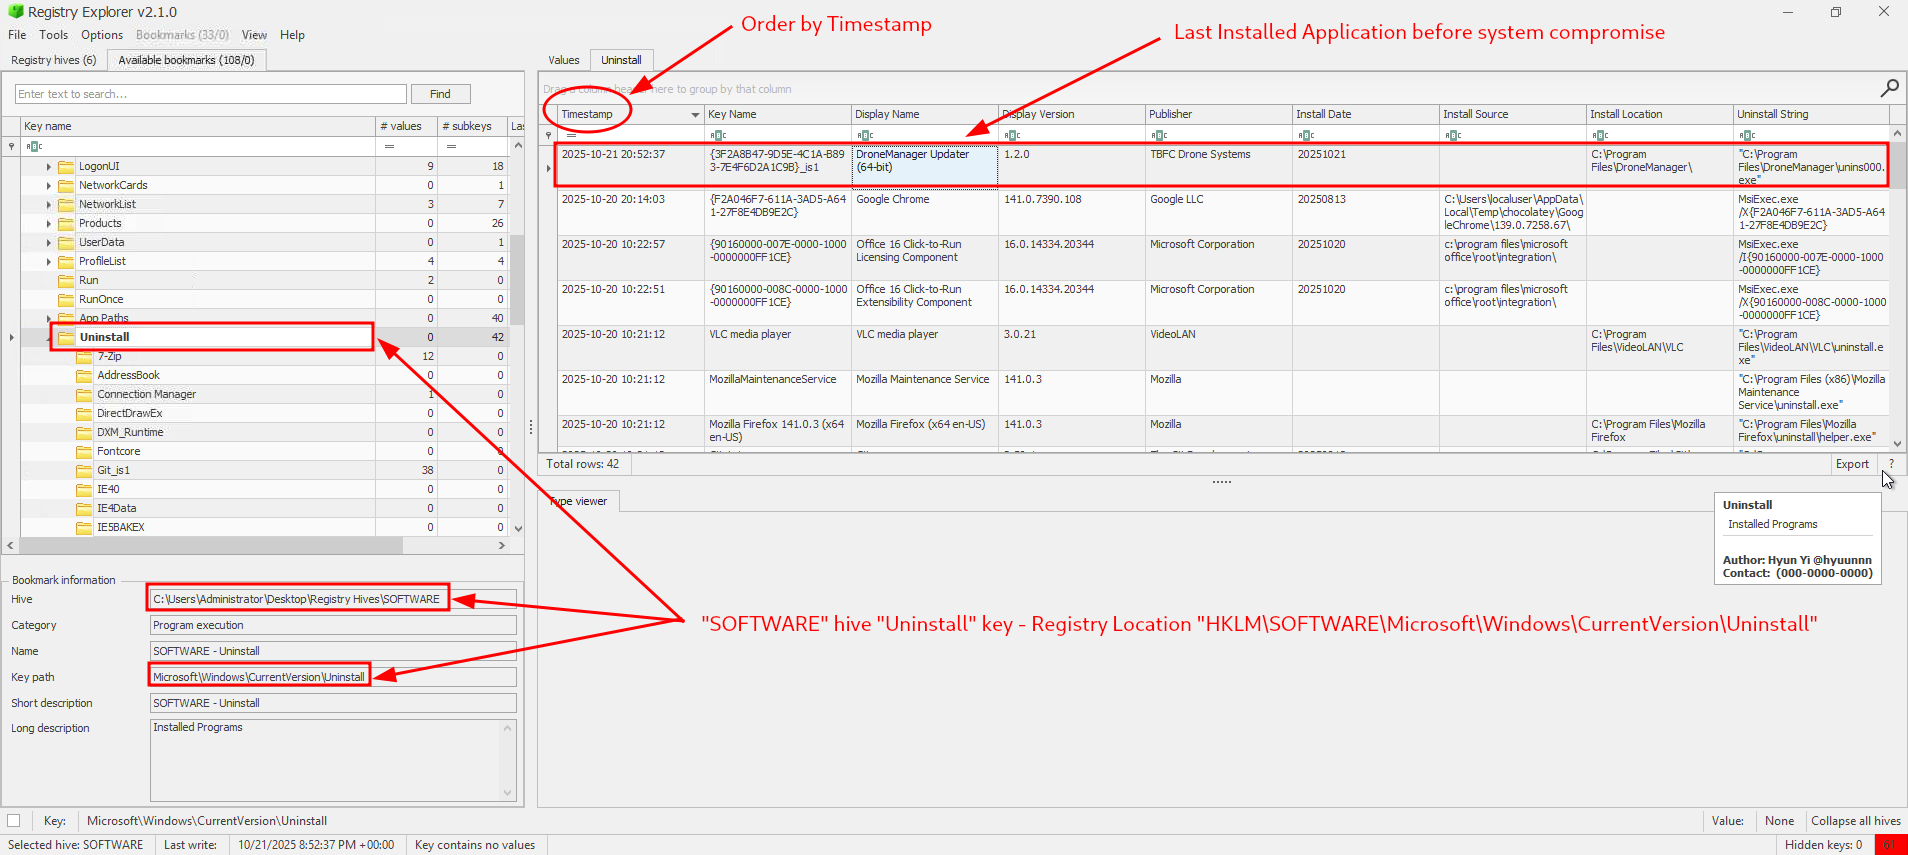
Figure 2: Registry Explorer displaying installed applications with timestamps showing DroneManager Updater as the last installed program
Given that the exercise explicitly notes that the time range starts only from 2025.11.21 on, the entry dated 2025-10-21 20:52:37 by DroneManager Updater (64bit) must be the clear answer here.
Question-2: What is the full path where the user launched the application (found in question 1) from?
C:\Users\dispatch.admin\Downloads\DroneManager_Setup.exe
We can check the recently accessed GUI-launched applications via HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\UserAssist, orienting ourselves by the Program Name and the Last Executed columns to further narrow down our search.
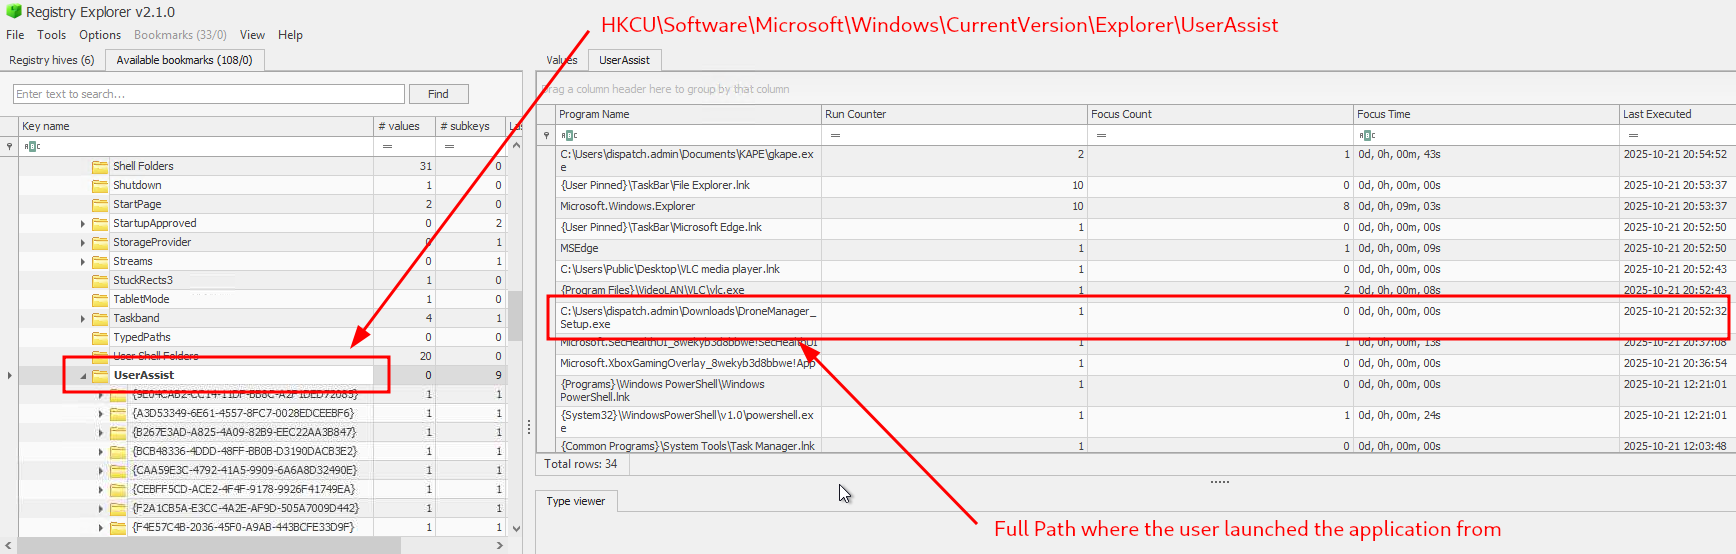
Figure 3: UserAssist registry key showing the full path where the user launched the DroneManager installer
Question-3: Which value was added by the application to maintain persistence on startup?
"C:\Program Files\DroneManager\dronehelper.exe" --background
First, we know that the keys for startup programs that are configured for automatic launch are stored in HKLM\Software\Microsoft\Windows\CurrentVersion\Run, so let us head over there:
C:\Users\Administrator\Desktop\Registry Hives\SOFTWARE > CurrentVersion > Run.
There are only two entries configured here, and the one with the name drone_helper should be the clear winner.
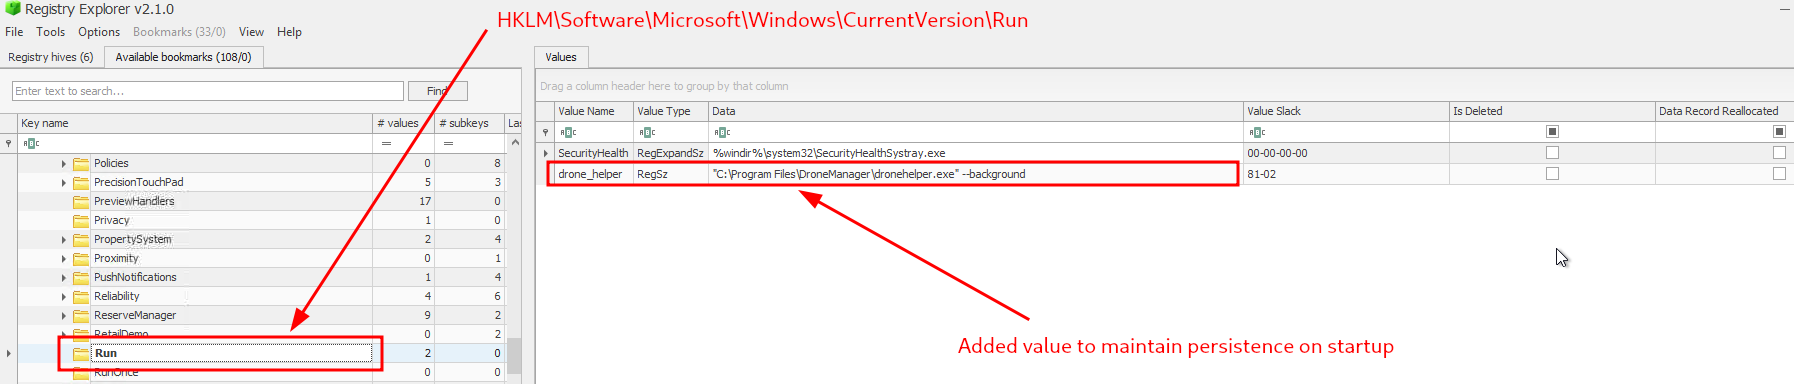
Figure 4: Run registry key showing the drone_helper entry configured to maintain persistence on startup
Question-4: If you enjoyed today’s room, feel free to check out the Expediting Registry Analysis room.
No answer needed