CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 20 Title: Race Conditions - Toy to The World |
Description
Learn how to exploit a race condition attack to oversell the limited-edition SleighToy.
Summary
We exploit race conditions where multiple simultaneous requests access shared resources before the system updates them. We configure Burp Suite to duplicate a checkout request 15 times and send all copies in parallel, triggering a timing flaw that processes multiple orders before inventory updates. We successfully oversell limited items and obtain the challenge flags.
Storyline
The Best Festival Company oversold a limited-edition SleighToy due to a checkout system timing flaw that allowed simultaneous purchases of only ten available pieces. Sir Carrotbane’s Bandit Bunnies exploited the vulnerability with rapid clicks, and investigator McSkidy uncovered how milliseconds of delay caused the inventory crisis.
Theory
Race conditions occur when multiple simultaneous actions compete to access or modify shared resources, and the system’s outcome depends on their execution order.
In web applications, this can lead to duplicate transactions, oversold inventory, or unauthorized data changes. There are three main types.
Main Types
Time-of-Check to Time-of-Use (TOCTOU)
- Data changes between when it is checked and when it is used.
- Two users buy the same last item simultaneously because stock was checked before updating.
Shared Resource
- Multiple users modify the same data without proper controls; the last update wins.
- Two cashiers updating the same spreadsheet, one overwriting the other’s work.
Atomicity Violation
- Part of a process completes while another request interrupts, causing inconsistency.
- Payment records but order confirmation fails due to a price change mid-transaction.
Mitigation Strategies
- Use atomic database transactions to bundle stock deduction and order creation as a single operation.
- Validate stock availability immediately before committing transactions.
- Implement idempotency keys to prevent duplicate request processing.
- Apply rate limiting and concurrency controls to block rapid repeated attempts.
Practice
Steps to Exploit a Race Condition
Steps to exploit a race condition in a shopping cart application:
Setup – Configure Firefox to route traffic through Burp Suite or use its default browser.
Capture – Make a legitimate checkout request and capture it; view it in Burp’s HTTP history.
Proxy > HTTP history > select the specific POST request > right-click then Send to Repeater.
- Duplicate – Create 15 identical copies of the checkout request.
In Repeater > right-click then Add tab to group > Create tab group > name it > right-click then Duplicate tab > enter the number of copies you want.
- Execute – Send all requests simultaneously using Send group in parallel.
Send dropdown in Repeater > Send group in parallel (last-byte sync)
- Sets the Send configuration to launch all copies at once and to wait for the final byte from each response, which maximizes the timing overlap to trigger race conditions.
Send dropdown in Repeater > Send group (parallel)
- Actually launches all requests simultaneously: the server attempting to handle them simultaneously triggers the timing bug (multiple orders being processed at once).
- Result – The server processes multiple orders before updating inventory, allowing overselling and driving stock into negative values.
Attacking the TBFC Shop
Step-1: Setup
Regarding the questions, for step 1, let us use Burp Suite’s built-in Chromium browser.
Launch Burp Suite, head over to the Proxy tab, use the Intercept sub-tab, and then click on Open browser. Make sure intercept is turned off.
Step-2: Capture
For step 2, we use the credentials:
- Username: attacker
- Password: attacker@123
Once logged in, make the sample purchase: Add to cart > Checkout > Confirm & Pay.
Then we head over to the Proxy tab in Burp Suite, select the specific POST request, and send it to Repeater:
Proxy > HTTP history > select the specific POST request > right-click then Send to Repeater.
Step-3: Duplicate
Moving on to step 3, use the following guide to create 15 copies of the specific POST request:
- In Repeater > right-click then Add tab to group > Create tab group > name it > right-click then Duplicate tab > enter 15 as the number of copies you want.
Step-4: Execute
Then, in step 4, it is time to finally send the requests and exploit the race condition vulnerability:
Send dropdown in Repeater > Send group in parallel (last-byte sync) will select the desired Send configuration.
Send dropdown in Repeater > Send group (parallel) will actually send them in parallel.
Step-5: Result
As for step 5, let us move back to our browser and refresh the shopping web application. We are provided with a flag if the race condition for that specific item was successfully exploited.
This is how it looks for the SleighToy Limited Edition item, which provides us with the first flag:
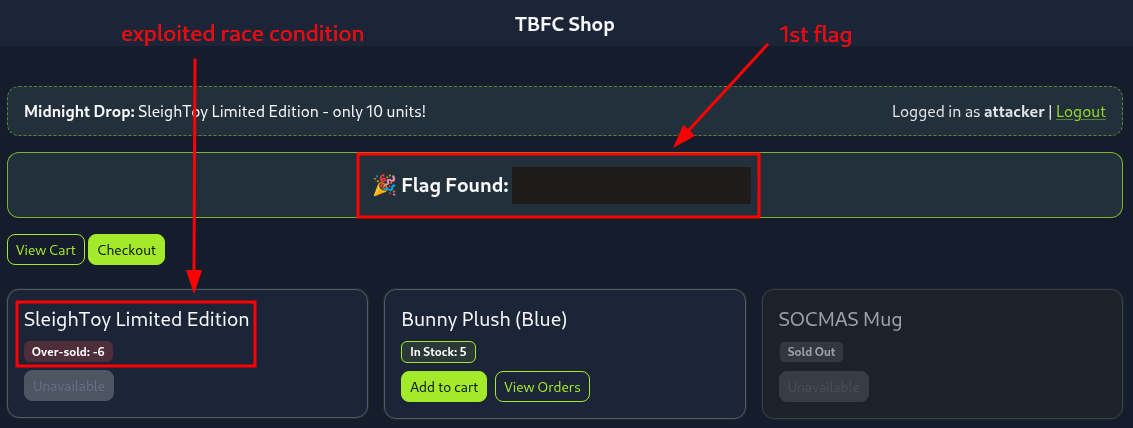
Figure 1: Web application showing negative stock count for SleighToy Limited Edition with flag displayed
Then we repeat steps 1 through 5 again for the Bunny Plush (Blue) item, landing us the second flag:
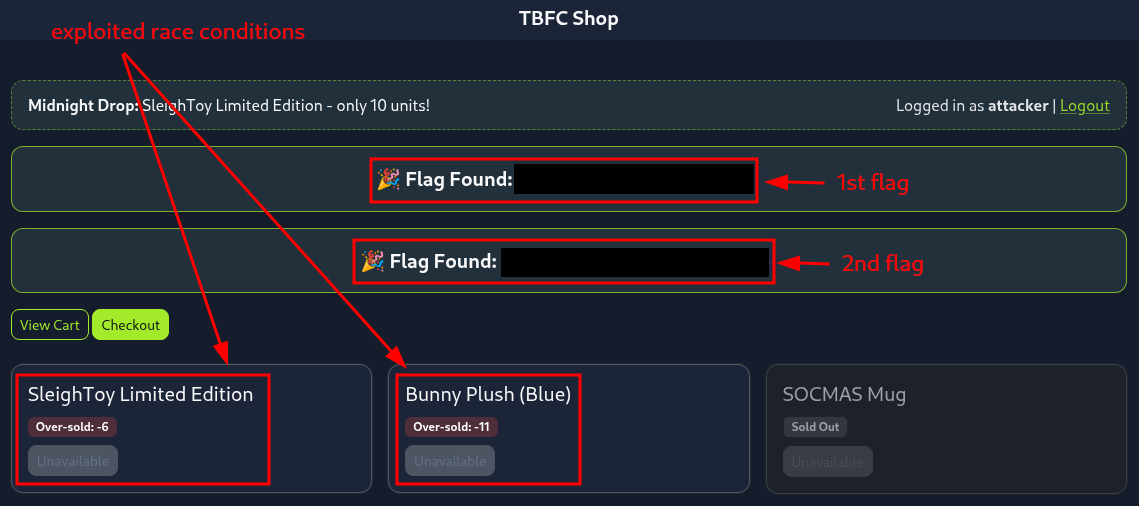
Figure 2: Web application showing negative stock count for Bunny Plush Blue with flag displayed
Questions and Answers
Question-1: What is the flag value once the stocks are negative for SleighToy Limited Edition?
<redacted-flag>
Question-2: Repeat the same steps as were done for ordering the SleighToy Limited Edition. What is the flag value once the stocks are negative for Bunny Plush (Blue)?
<redacted-flag>
Question-3: Feel free to check out the Race Conditions room if you enjoyed this task.
No answer needed