CHALLENGE INFORMATION
 | Platform: TryHackMe Event: Advent of Cyber 2025 Day: 22 Title: C2 Detection - Command & Carol |
Description
We explore how to analyze large PCAP files and extract valuable threat intelligence.
Summary
We begin with an overview of RITA (Real Intelligence Threat Analytics), examining how it detects malicious network activity by analyzing Zeek logs and identifies threats through network pattern analysis and severity scoring.
Practically, we convert PCAP files to Zeek logs, import them into RITA, and access the viewer interface.
Finally, we employ RITA’s filtering capabilities to analyze the data, applying search filters, examining prevalence scores, reviewing connection counts and ports, and sorting by metrics to uncover suspicious network behavior.
Storyline
The TBFC, on high alert after King Malhare’s attacks, grows restless in the quiet. Sir Elfo proposes hunting for Command and Control traffic using RITA (Real Intelligence Threat Analytics), a tool that can quickly analyze their network data by converting PCAP files to Zeek logs.
Theory
RITA (Real Intelligence Threat Analytics) is an open-source framework by Active Countermeasures that detects malicious network activity by analyzing Zeek logs.
It identifies threats like command and control (C2) communication, DNS tunneling, data exfiltration, and long connections through correlation of network data fields such as IP addresses, ports, timestamps, and connection durations.
Key Capabilities
RITA analyzes network patterns to detect periodic connections, excessive DNS queries, random subdomains, unusual certificate behavior, and known malicious IPs from threat intelligence feeds. It then scores connections by severity and presents findings in a searchable terminal interface.
How It Works
It requires Zeek logs as input – Zeek is a network security monitoring tool that converts packet captures (PCAPs) into structured, enriched logs.
We import these logs into RITA using the command line, and RITA parses and analyzes the data to produce results.
RITA Interface/GUI
The RITA viewer displays results in three sections:
- Search bar: Allows filtering with support for specific search fields.
- Results Pane: Shows severity scores, source/destination IPs, beacon likelihood, connection duration, subdomains, and threat intelligence matches.
- Details Pane: Contains threat modifiers (such as MIME type mismatches, rare signatures, prevalence analysis, and unusual data volumes) and connection metadata (connection counts, bytes sent, port numbers, and protocols).
Practical
Convert PCAP to Zeek logs
We first check the available data in the two directories, pcaps and zeek_logs:
ubuntu@tryhackme:~$ ls -hla pcaps/ zeek_logs/
pcaps/:
...
-rw-r--r--  1 ubuntu ubuntu  43M ... AsyncRAT.pcap
-rw-r--r--  1 ubuntu ubuntu  41M ... IcedID.pcap
-rw-r--r--  1 ubuntu ubuntu 7.1M ... Pikabot.pcap
-rw-r--r--  1 ubuntu ubuntu 113K ... rita_challenge.pcap
...
zeek_logs/:
-rw-rw-r--  1 ubuntu docker  14M ... Example-5-2020-08-18-Emotet-infection-with-Qakbot.pcap.zip
drwxr-xr-x  2 ubuntu ubuntu 4.0K ... asyncrat
drwxr-xr-x  2 ubuntu ubuntu 4.0K ... pikabot
ubuntu@tryhackme:~$
Next, we use Zeek to parse and convert – zeek readpcap <pcap-file> <output-directory> – the PCAP data into structured log format:
ubuntu@tryhackme:~$ mkdir zeek_logs/rita-challenge
ubuntu@tryhackme:~$ zeek readpcap pcaps/rita_challenge.pcap zeek_logs/rita-challenge
Starting the Zeek docker container
Zeek logs will be saved to /home/ubuntu/zeek_logs/rita-challenge
ubuntu@tryhackme:~$
The following listing shows the transformed logs:
ubuntu@tryhackme:~$ ls -hla zeek_logs/rita-challenge/
...
-rw-r--r-- 1 root   root    488 ... analyzer.log
-rw-r--r-- 1 root   root    542 ... capture_loss.log
-rw-r--r-- 1 root   root    47K ... conn.log
-rw-r--r-- 1 root   root   3.6K ... dns.log
-rw-r--r-- 1 root   root   4.4K ... files.log
-rw-r--r-- 1 root   root    35K ... http.log
-rw-r--r-- 1 root   root    317 ... known_hosts.log
-rw-r--r-- 1 root   root    527 ... known_services.log
-rw-r--r-- 1 root   root    35K ... loaded_scripts.log
-rw-r--r-- 1 root   root   1.6K ... notice.log
-rw-r--r-- 1 root   root    278 ... packet_filter.log
-rw-r--r-- 1 root   root    379 ... reporter.log
-rw-r--r-- 1 root   root   1000 ... software.log
-rw-r--r-- 1 root   root   2.1K ... stats.log
-rw-r--r-- 1 root   root   2.9K ... weird.log
ubuntu@tryhackme:~$
If necessary, we can search for more information on the specific log files via their documentation.
Import Log Data into RITA
We use RITA to import, parse, and analyze the newly created logs:
ubuntu@tryhackme:~$ rita import --logs zeek_logs/rita-challenge/ --database ritachallenge
...
✔ Container rita-syslog-ng
✔ Container rita-clickhouse
✔ Container rita-syslog-ng
...
Container rita-rita-run-2493b7e1ece6 Creating
Container rita-rita-run-2493b7e1ece6 Created
... INF Initiating new import... dataset=ritachallenge directory=/tmp/zeek_logs rebuild=false rolling=false started_at="..."
[-] Parsing:  /tmp/zeek_logs/conn.log
[-] Parsing:  /tmp/zeek_logs/http.log
[-] Parsing:  /tmp/zeek_logs/dns.log
...
[+] stop 1/1
✔ Container rita-rita-1 Stopped
....
ubuntu@tryhackme:~$
With the import complete, we access the data using rita view <database-name>:
ubuntu@tryhackme:~$ rita view ritachallenge
...
Container rita-clickhouse Waiting
Container rita-clickhouse Healthy
Container rita-rita-run-a40a9aacc2eb Creating
Container rita-rita-run-a40a9aacc2eb Created
Viewing database: ritachallenge
The RITA GUI (within the terminal) will be displayed with data populated from the ritachallenge database.
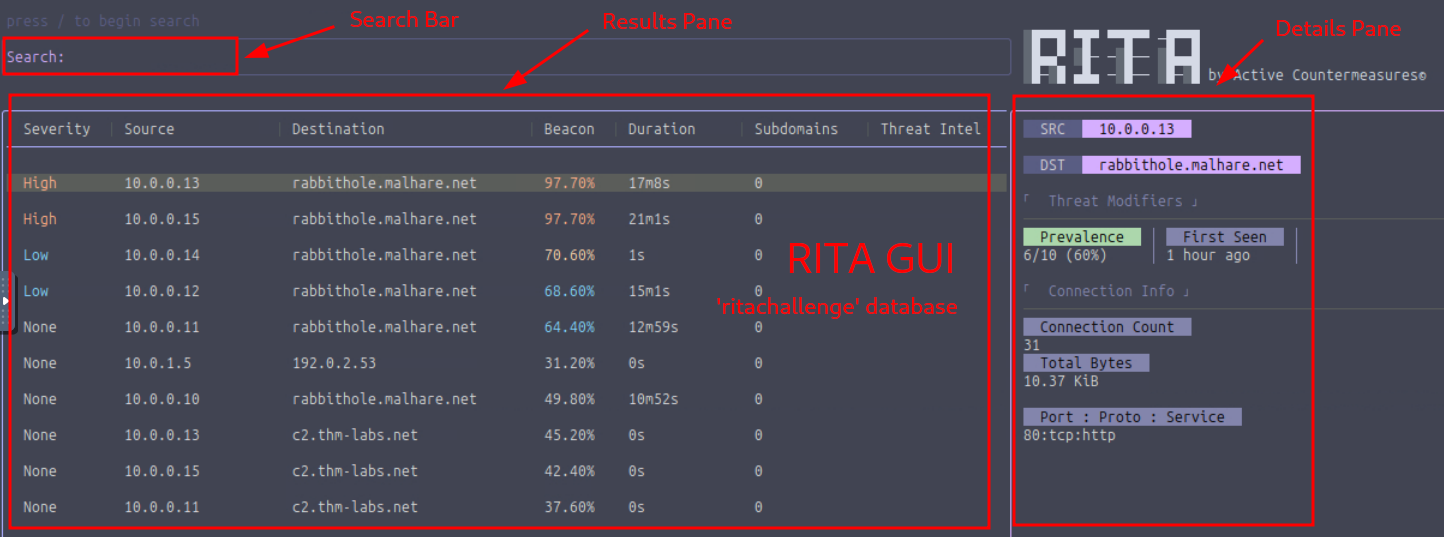
Figure 1: RITA terminal interface displaying network analysis results
Questions and Answers
Question-1: How many hosts are communicating with malhare.net?
6
Prevalence denotes the number of internal hosts communicating with a specific (here malhare.net) external host.
We select one entry within the target domain – such as rabbithole.malhare.net – and use the Details Pane to check its prevalence score.
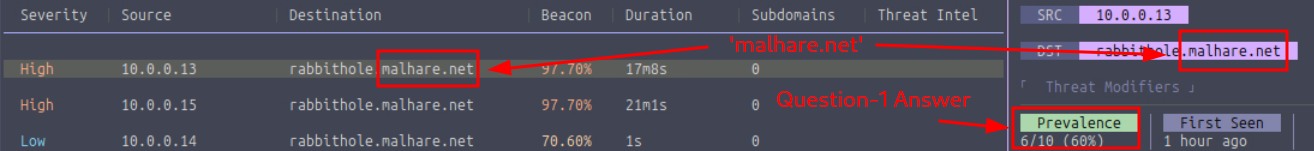
Figure 2: Prevalence score showing six internal hosts communicating with malhare.net
Question-2: Which Threat Modifier tells us the number of hosts communicating to a certain destination?
Prevalence
See the explanation for Question 1.
Question-3: What is the highest number of connections to rabbithole.malhare.net?
40
We use the filter dst:rabbithole.malhare.net to restrict the entries and use the Details Pane to search for the entry with the highest connection count.
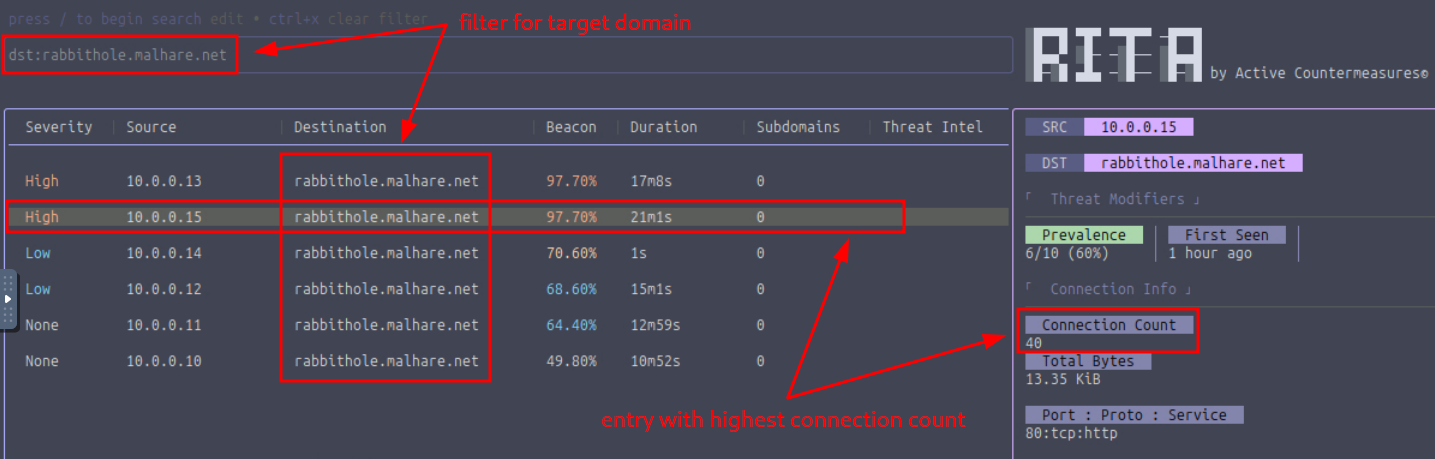
Figure 3: Connection details showing 40 connections to rabbithole.malhare.net
Question-4: Which search filter would you use to search for all entries that communicate to rabbithole.malhare.net with a beacon score greater than 70% and sorted by connection duration (descending)?
dst:rabbithole.malhare.net beacon:>=70 sort:duration-desc
Figure 4 shows the filtered results:
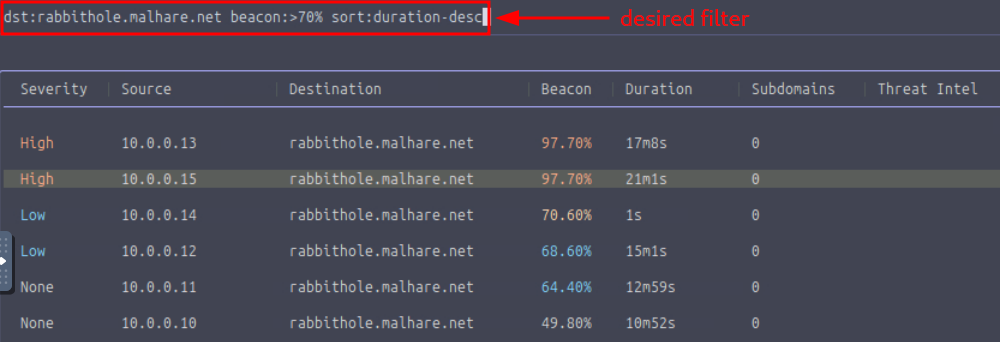
Figure 4: RITA search results filtered by destination and beacon score
Question-5: Which port did the host 10.0.0.13 use to connect to rabbithole.malhare.net?
80
We first locate and select the internal host 10.0.0.13 using the Source column, then examine the Port:Proto:Service entry under the Connection Info section in the Details Pane.
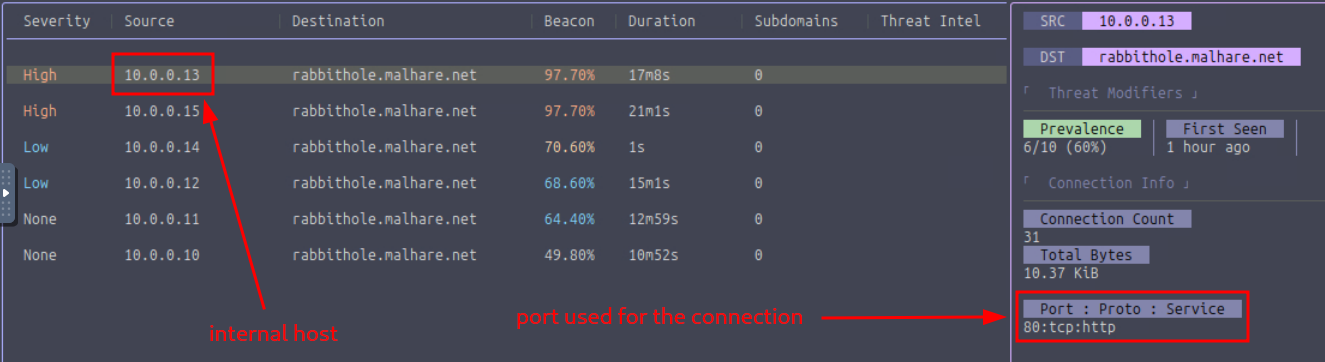
Figure 5: Connection details revealing port 80 used by host 10.0.0.13