CHALLENGE INFORMATION
Platform: TryHackMe
Path: CompTIA PenTest+
Room: Nessus
Description: Learn how to set up and use Nessus, a popular vulnerability scanner.
Introduction
Read the short introduction before moving to the next task.
Question 1: I have read the description!
No answer needed
Installation
Here, we will install Nessus on a Kali system. Follow the guide through the steps. First, let us register for the activation code.
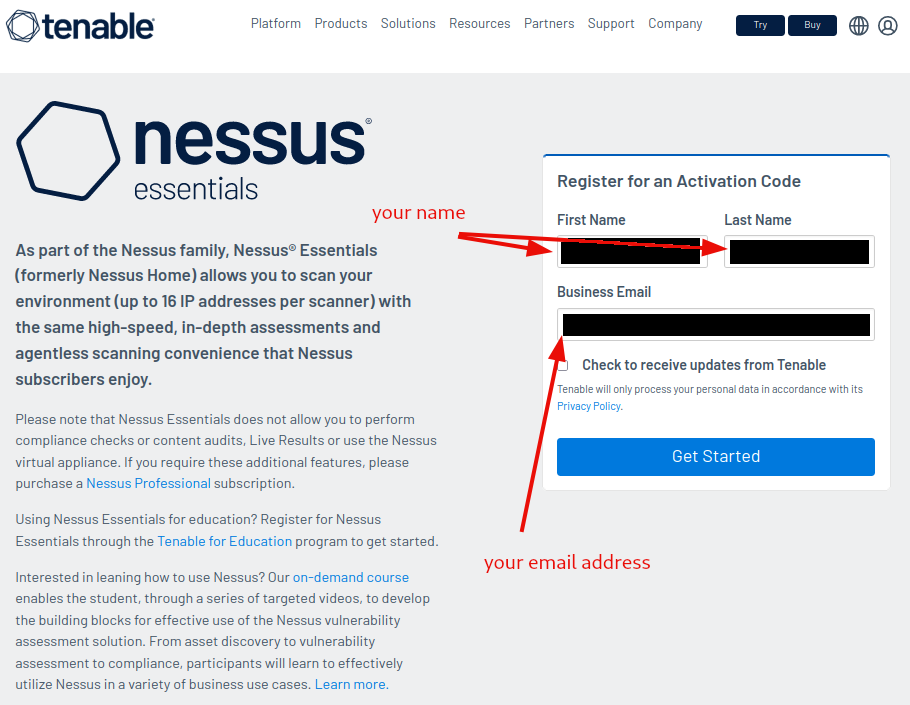
Figure 1: Activation code registration for Tenable Nessus
Verify that you actually received the activation code by checking your email, and download the Nessus program.
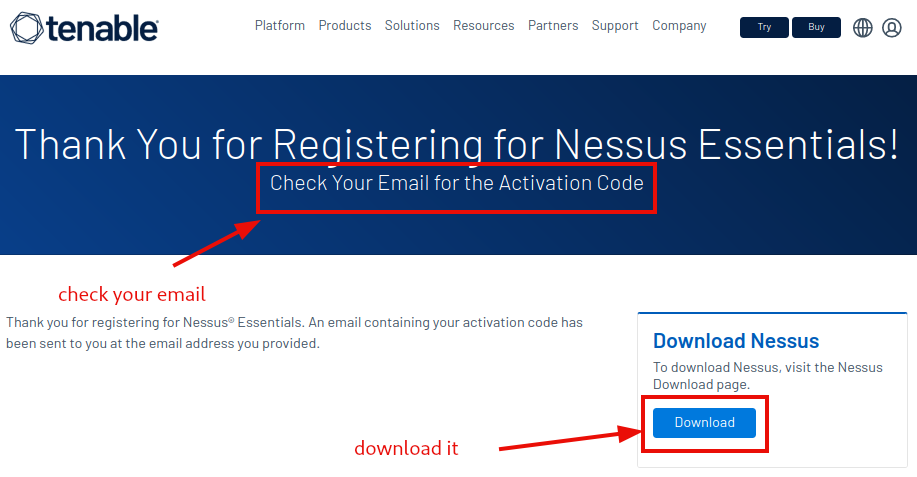
Figure 2: Verifying activation code registration
Select your platform and download the software.
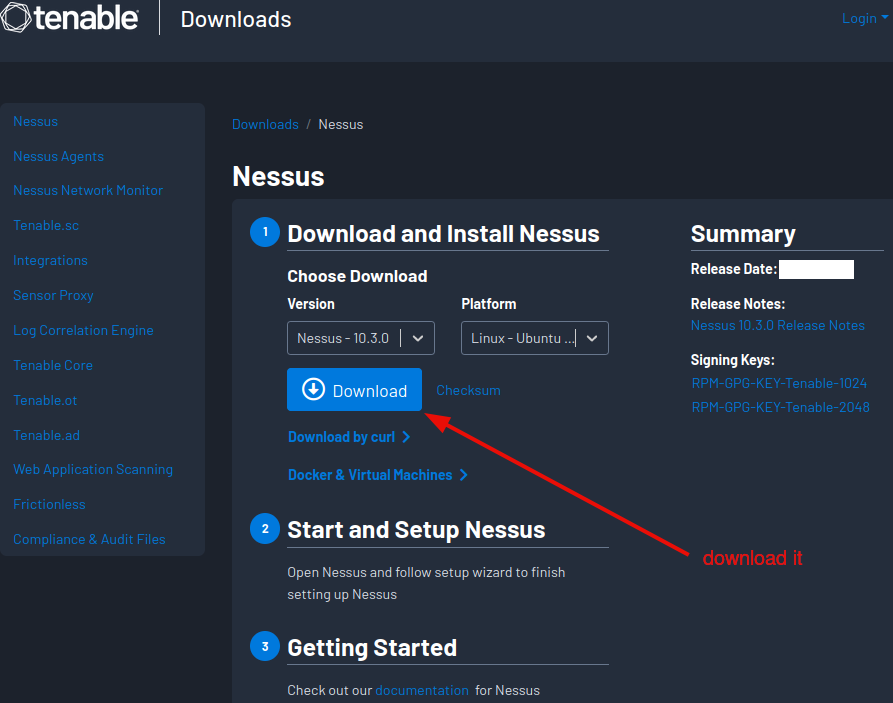
Figure 3: Customizing Nessus download
Accept the license agreement.
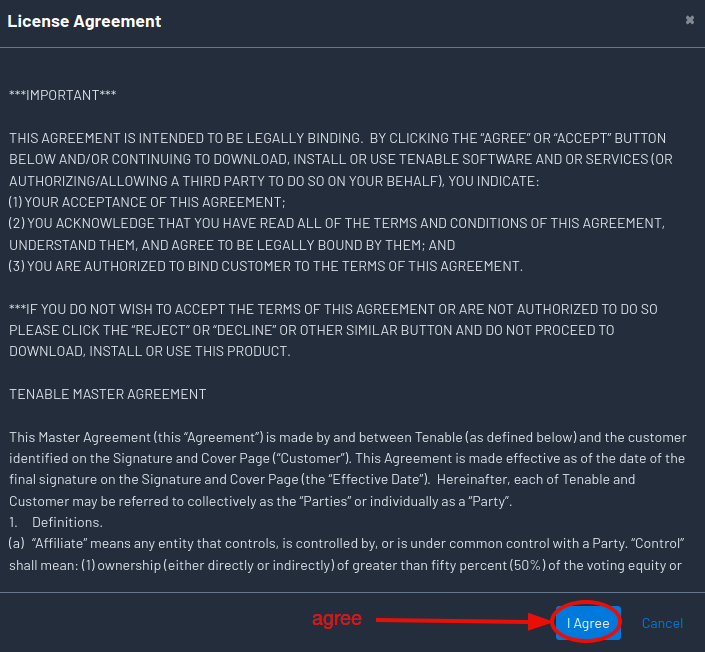
Figure 4: Accepting the terms and conditions
Optional: Download the checksum to verify the integrity of your software download.
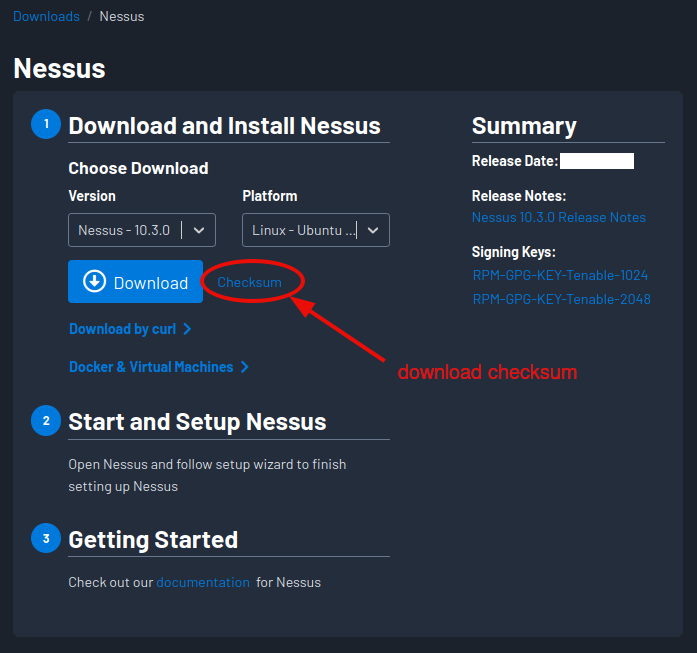
Figure 5: Checksum download for verification
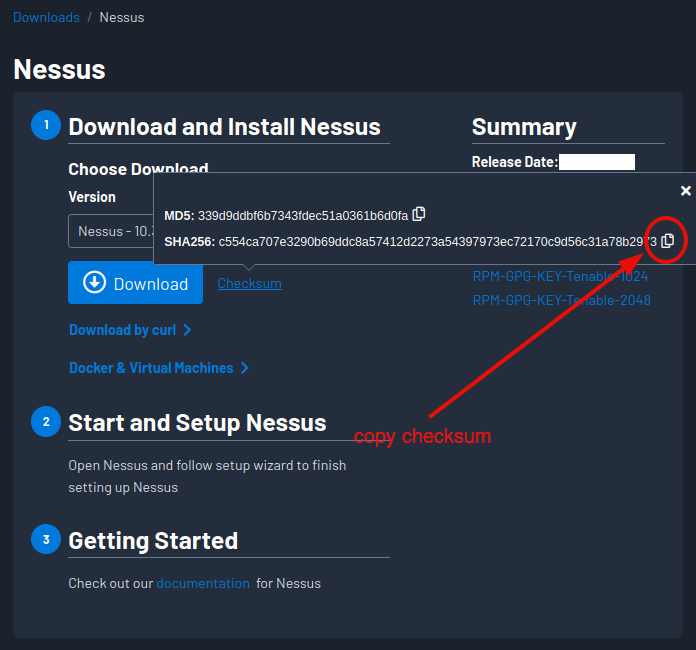
Figure 6: Copying the SHA256 checksum
Write the hash to a simple text file, appending the program’s name with two spaces in between. (This allows us to automatically check for a match.)
echo "c554ca707e3290b69ddc8a57412d2273a54397973ec72170c9d56c31a78b2973 Nessus-10.3.0-ubuntu1404_amd64.deb" > nessus.hash
Then, generate the hash for the Nessus .deb file (using sha256sum for SHA256 hashes) and append it to our hash file –nessus.hash.
sha256sum Nessus-10.3.0-ubuntu1404_amd64.deb >> nessus.hash
Finally, we can either manually verify that the hashes match by simply checking the hash file,
cat nessus.hash
or by using sha256sum’s built-in check function.
sha256sum --check nessus.hash
Complete terminal interaction:
user@kali:~$ echo "c554ca707e3290b69ddc8a57412d2273a54397973ec72170c9d56c31a78b2973  Nessus-10.3.0-ubuntu1404_amd64.deb" > nessus.hash
user@kali:~$ sha256sum Nessus-10.3.0-ubuntu1404_amd64.deb >> nessus.hash
user@kali:~$ cat nessus.hash
c554ca707e3290b69ddc8a57412d2273a54397973ec72170c9d56c31a78b2973  Nessus-10.3.0-ubuntu1404_amd64.deb
c554ca707e3290b69ddc8a57412d2273a54397973ec72170c9d56c31a78b2973  Nessus-10.3.0-ubuntu1404_amd64.deb
user@kali:~$ sha256sum --check nessus.hash
Nessus-10.3.0-ubuntu1404_amd64.deb: OK
Nessus-10.3.0-ubuntu1404_amd64.deb: OK
user@kali:~$As we see, everything checks out, so we can safely proceed with the installation.
Install the package:
sudo dpkg -i Nessus-10.3.0-ubuntu1404_amd64.deb
Terminal output:
user@kali:~$ sudo dpkg -i Nessus-10.3.0-ubuntu1404_amd64.deb
[sudo] password for user:
Selecting previously unselected package nessus.
(Reading database ... 371004 files and directories currently installed.)
Preparing to unpack Nessus-10.3.0-ubuntu1404_amd64.deb ...
Unpacking nessus (10.3.0) ...
Setting up nessus (10.3.0) ...
Unpacking Nessus Scanner Core Components...

 - You can start Nessus Scanner by typing /bin/systemctl start nessusd.service
 - Then go to https:/kali:8834/ to configure your scanner

user@kali:~$Start the Nessus service:
sudo /bin/systemctl start nessusd.service
After the service daemon is started, open https://localhost:8834/ in your web browser. Here we use https://kali:8834/, because we use kali as the hostname on our system, but it should not make any difference.
Follow the instructions through steps #5 - #8 to finish the setup.
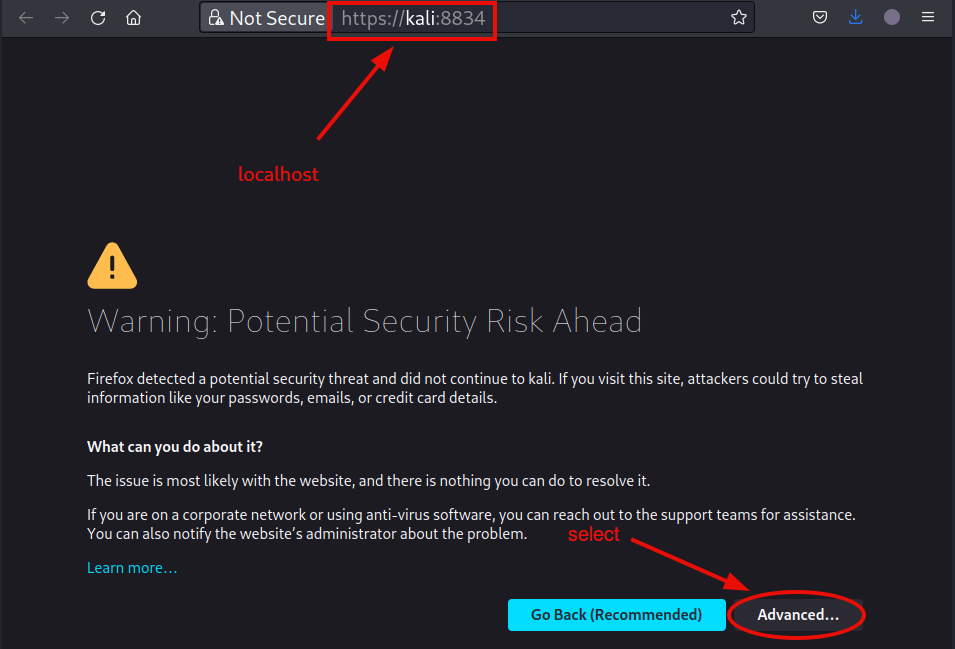
Figure 7 and 8: Browser certificate warning
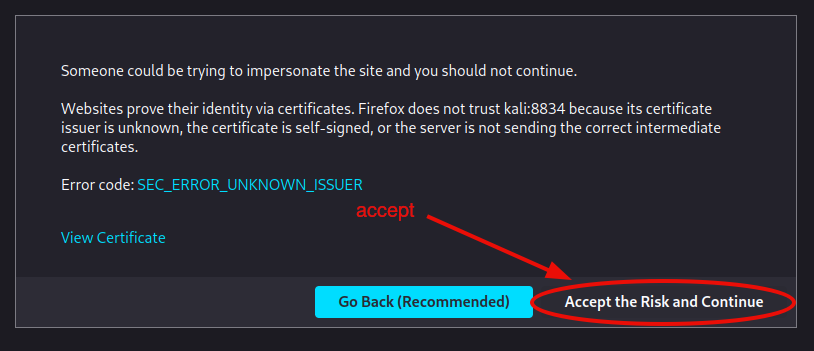
Figure 9: Workaround for browser certificate warning
Step #6: Set up the scanner.
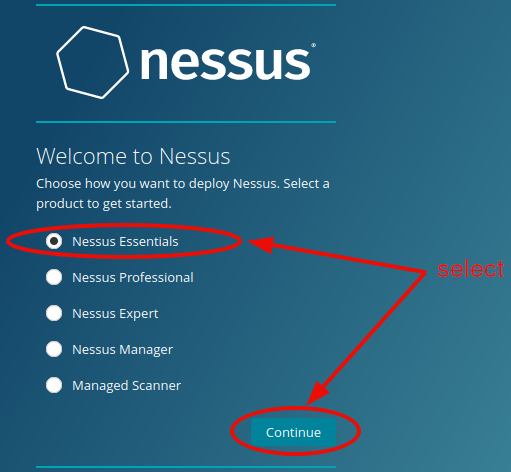
Figure 10: Choosing Nessus Essentials
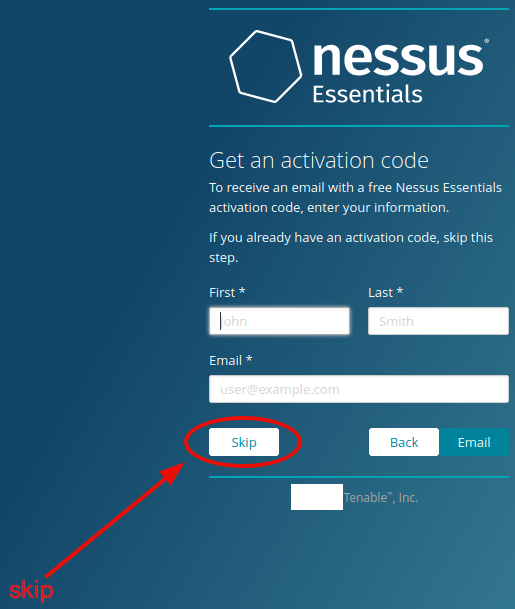
Figure 11: Skipping registration with installer
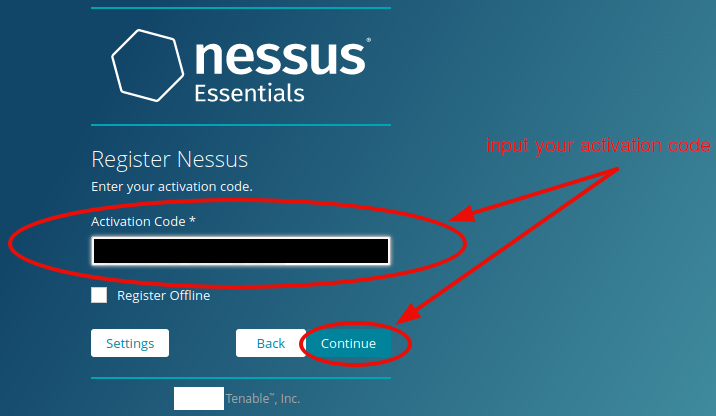
Figure 12: Entering previously registered activation code
Optional, set a proxy or encryption password. (We will leave it blank here.)
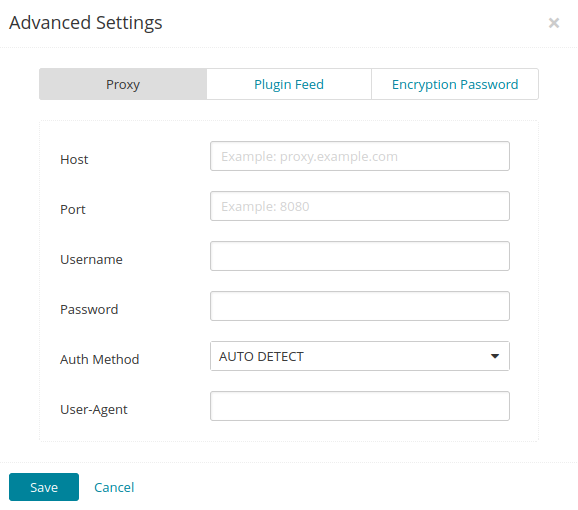
Figure 13: Optional settings
Step #7: Create account.
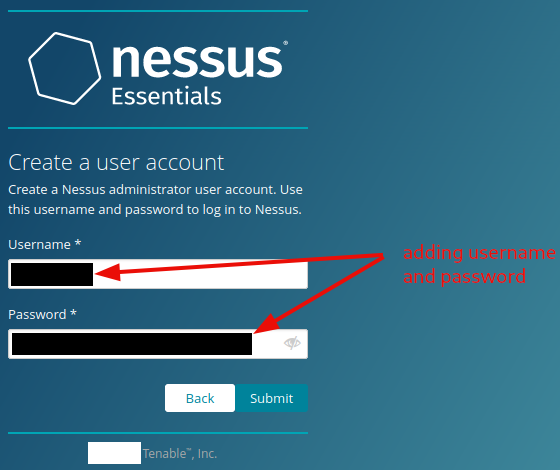
Figure 14: User account creation
Step #8: Install the plugins.
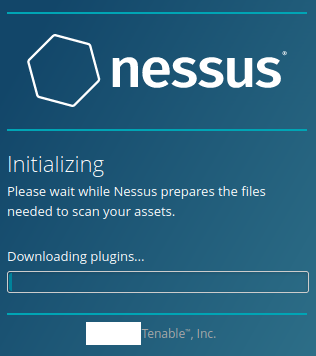
Figure 15: Plugin install
Step #9 and #10: Log in with the account credentials you created earlier, and enjoy your successful installation.
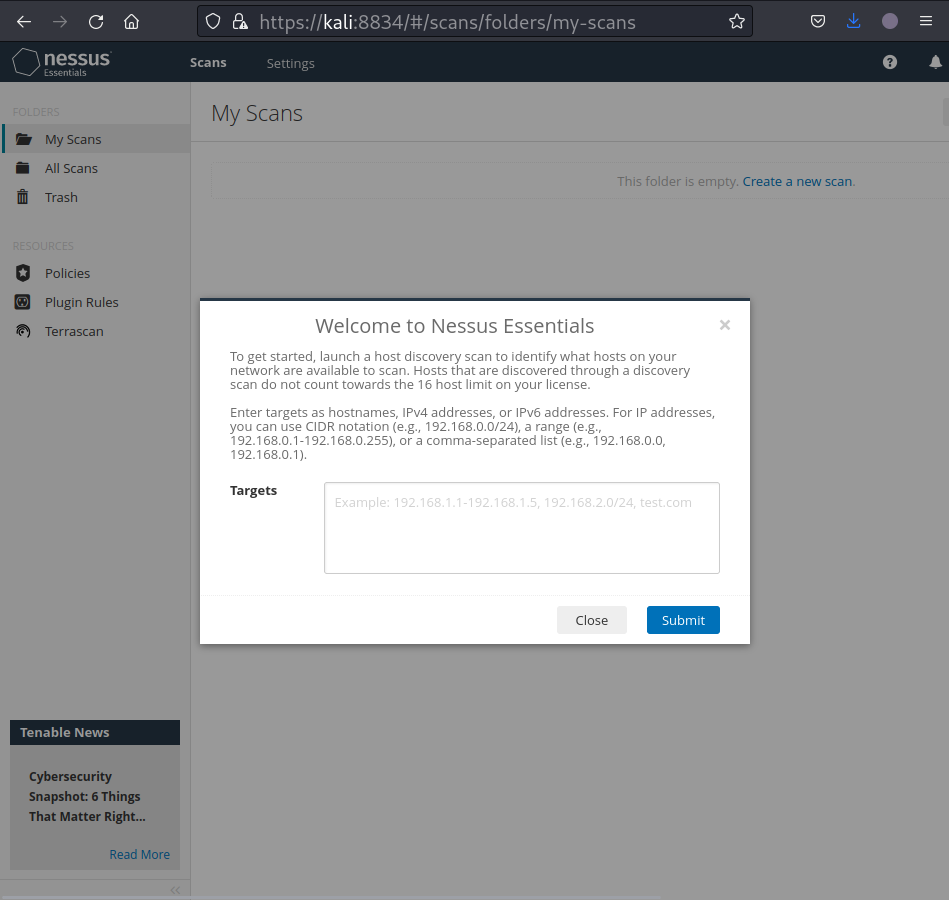
Figure 16: Welcome screen for Nessus Essentials
Question 1-10: Step #1-#10
No answer needed
Navigation and Scans
Answer the questions by moving around the site.
Question 1: What is the name of the button which is used to launch a scan?
New Scan
Figure 17: Starting a new scan
Question 2: What side menu option allows us to create custom templates?
Policies
Question 3: What menu allows us to change plugin properties such as hiding them or changing their severity?
Plugin Rules
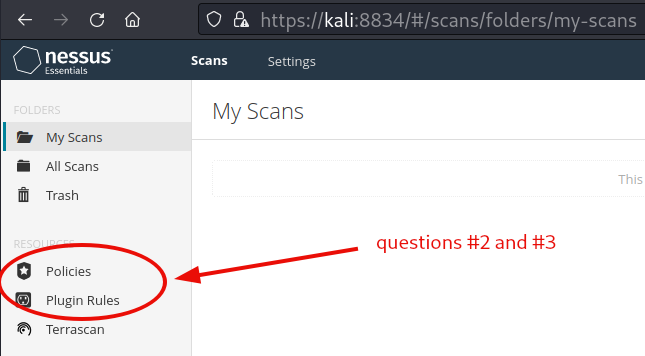
Figure 18: Placement for policies and plugin rules
Question 4: In the Scan Templates section after clicking on New Scan, what scan allows us to see simply what hosts are alive?
Host Discovery
Question 5: One of the most useful scan types, which is considered to be suitable for any host?
Basic Network Scan
Question 6: What scan allows you to Authenticate to hosts and enumerate missing updates?
Credentialed Patch Audit
Question 7: What scan is specifically used for scanning Web Applications?
Web Application Tests
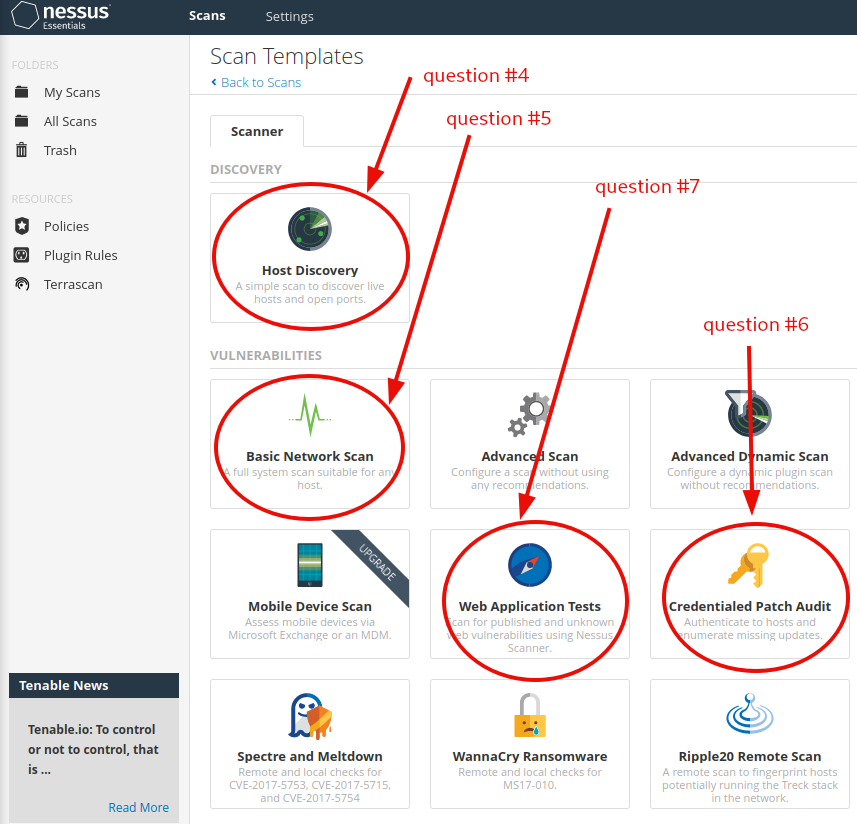
Figure 19: Available scan templates
Port Scanning
Remember to start the machine before performing any scans. Create a new scan, set the target, and configure the scan parameters.
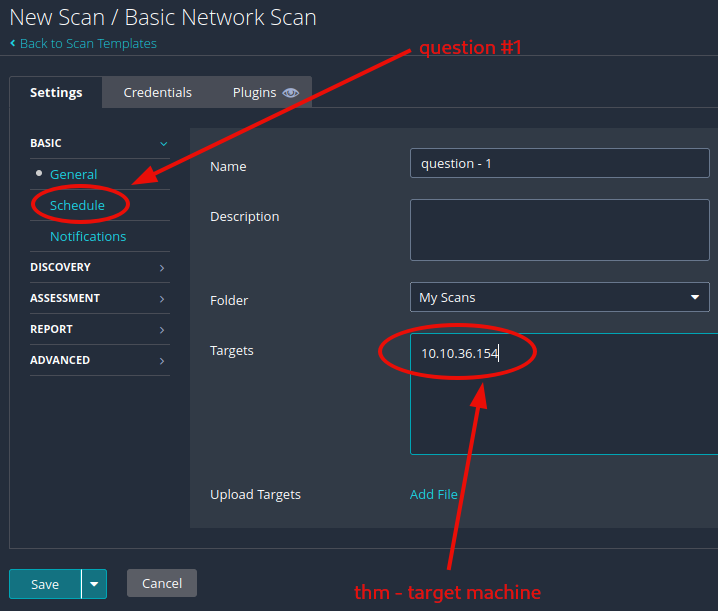
Figure 20: Specifying the target for a scan
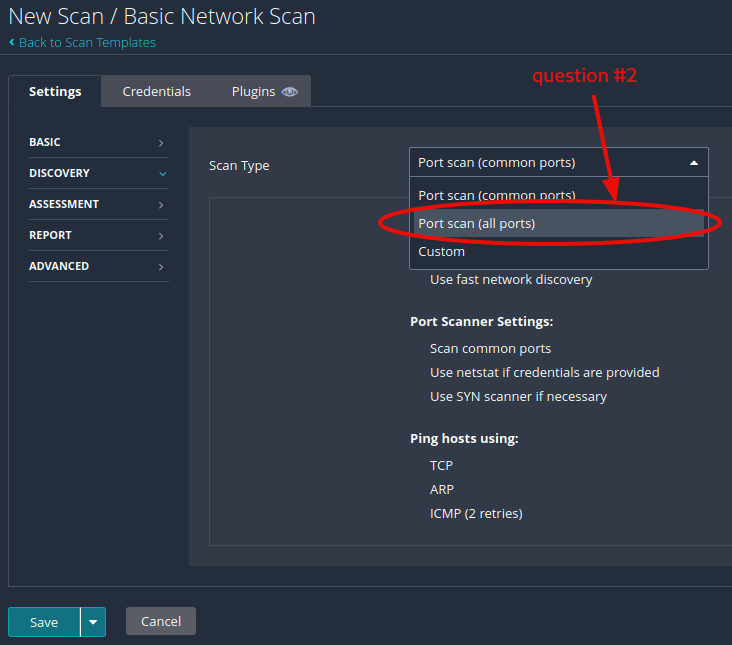
Figure 21: Specifying the scan type
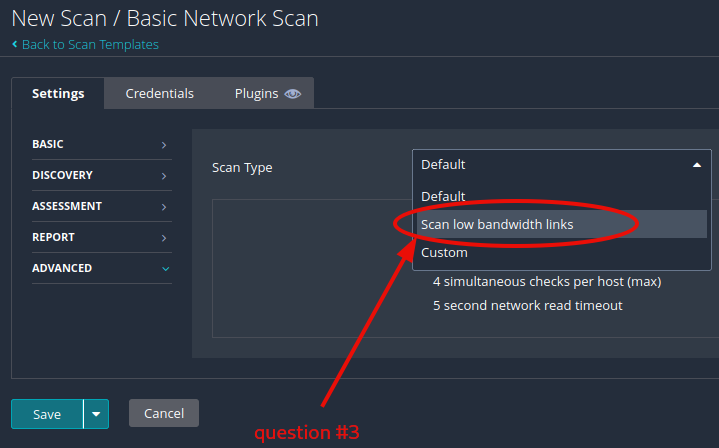
Figure 22: Available scan types
Launch the scan, and review the reported vulnerabilities.
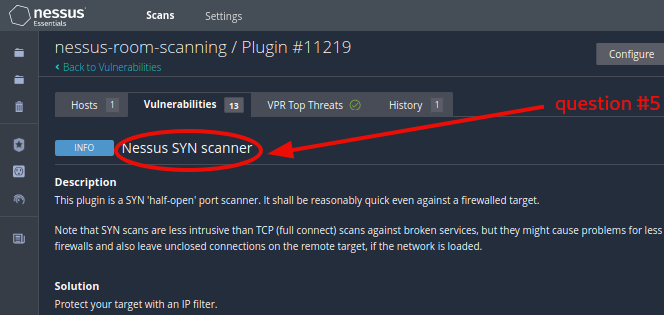
Figure 23: Reported vulnerabilities
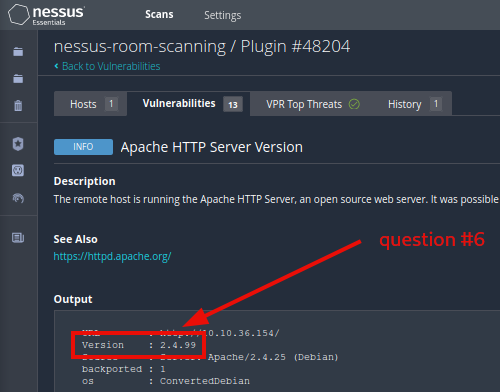
Figure 24: Vulnerable Apache server version
Question 1: Create a new Basic Network Scan targeting the deployed VM. What option can we set under BASIC (on the left) to set a time for this scan to run? This can be very useful when network congestion is an issue.
Schedule
Question 2: Under DISCOVERY (on the left) set the Scan Type to cover ports 1-65535. What is this type called?
Port scan (all ports)
Question 3: What Scan Type can we change to under ADVANCED for lower bandwidth connection?
Scan low bandwidth links
Question 4: With these options set, launch the scan.
No answer needed
Question 5: After the scan completes, which Vulnerability in the Port scanners family can we view the details of to see the open ports on this host?
Nessus SYN scanner
Question 6: What Apache HTTP Server Version is reported by Nessus?
2.4.99
Scanning a Web Application!
Make sure the started machine is still running. Launch a new Web Application scan. Once the results are in, try to answer the questions.
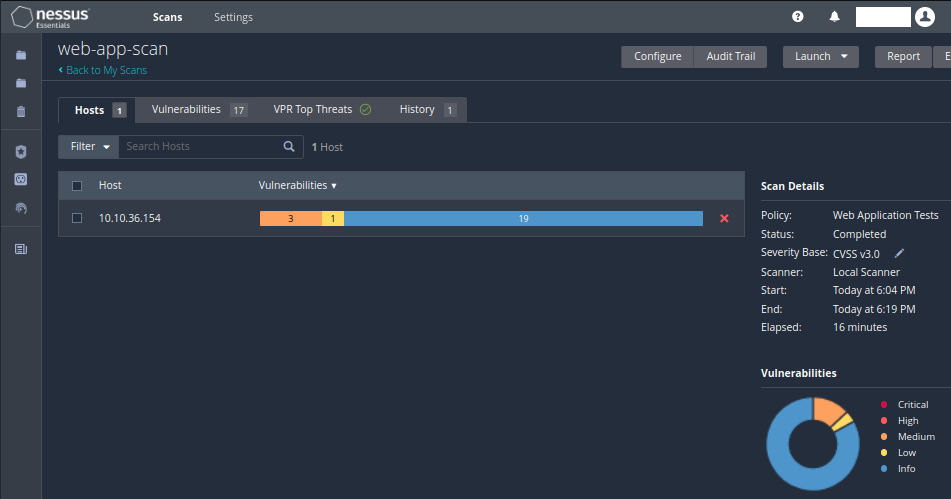
Figure 25: Web application scan
Question 1: What is the plugin id of the plugin that determines the HTTP server type and version?
10107
For the first one, check HTTP (Multiple Issues) in the Web Servers category.
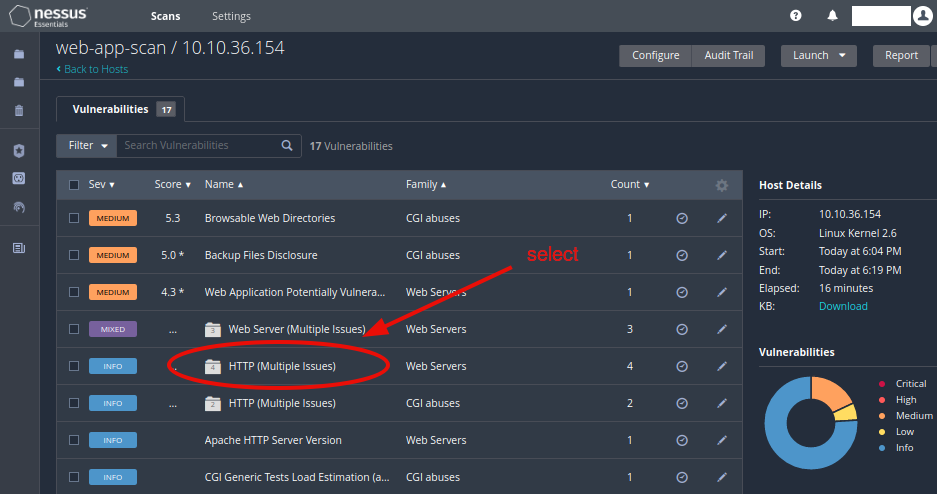
Figure 26: Results for web app scan
Then, open the one called HTTP Server Type and Version.
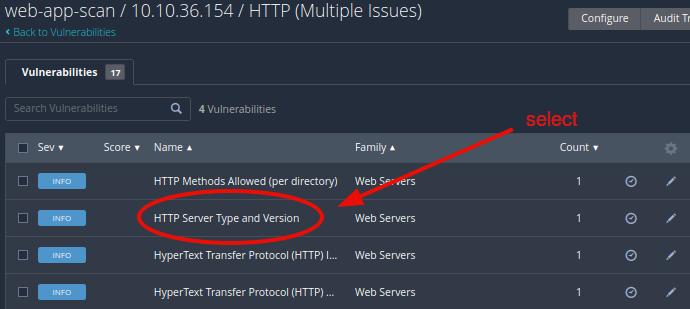
Figure 27: Drilling down on a specific vulnerability report
You will find the plugin ID both at the top of the page and on the right side under plugin details.
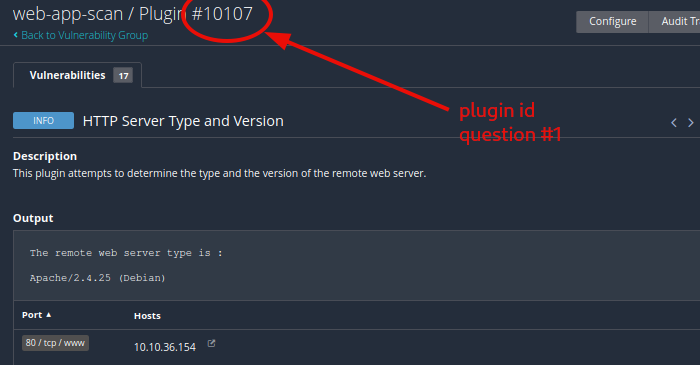
Figure 28: Plugin details
Question 2: What authentication page is discovered by the scanner that transmits credentials in cleartext?
login.php
The Web Server (Multiple Issues) is the only one containing a vulnerability with low severity.
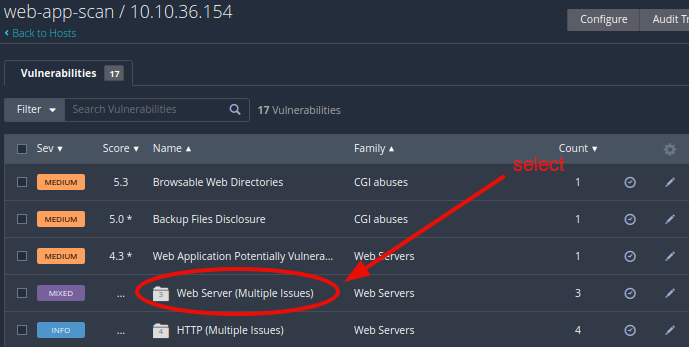
Figure 29: Web server (multiple issues) vulnerability
Head over and check out the one named Web Server Transmits Cleartext Credentials.
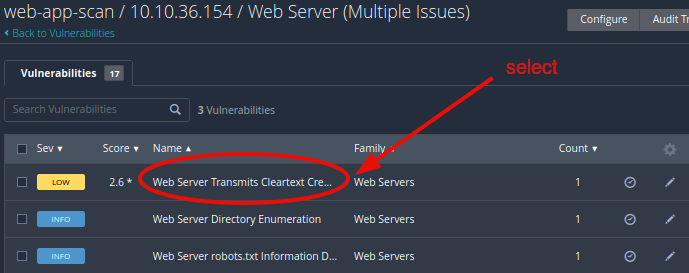
Figure 30: Web server transmits cleartext credentials vulnerability
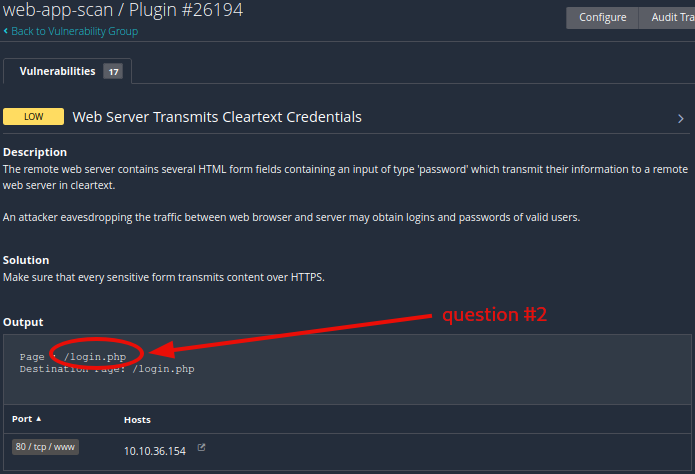
Figure 31: Output for the web server transmits cleartext credentials vulnerability
Question 3: What is the file extension of the config backup?
.bak
Under Backup Files Disclosure we will find the backup config file’s path and its full name.
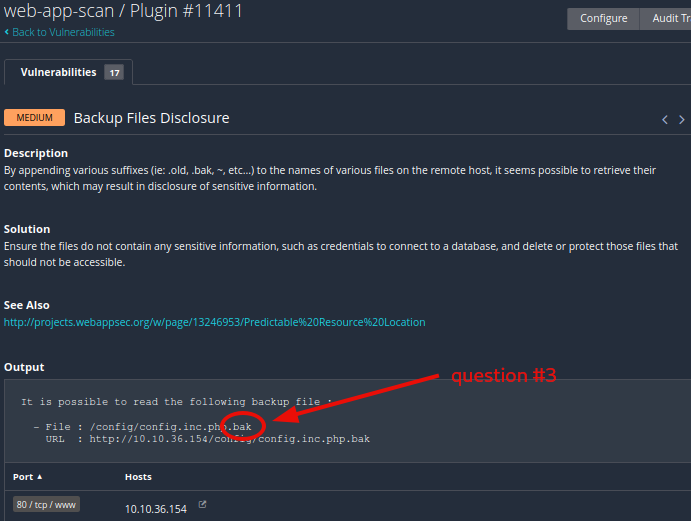
Figure 32: Full name of the backup config file
Question 4: Which directory contains example documents? (This will be in a php directory)
/external/phpids/0.6/docs/examples/
Under Browsable Web Directories, you will find the directory used to store the example documents.
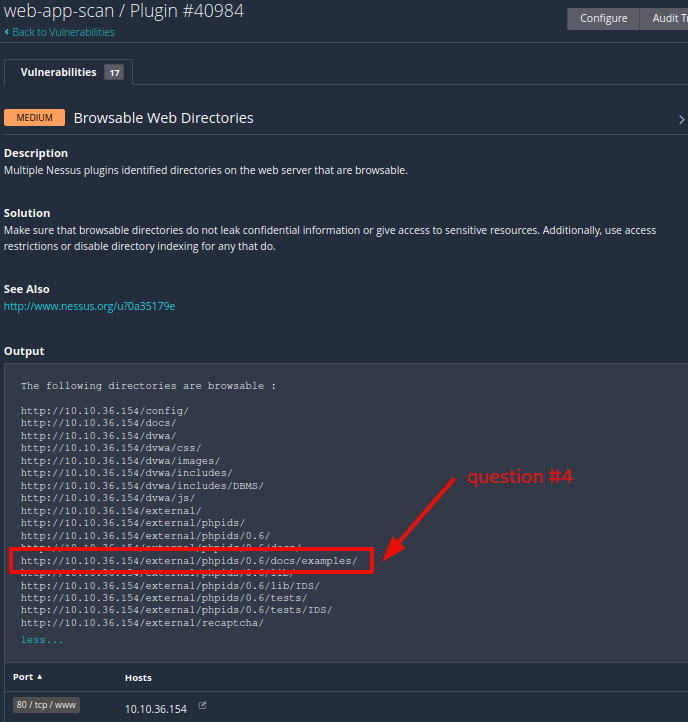
Figure 33: Directory for storing the example documents
Question 5: What vulnerability is this application susceptible to that is associated with X-Frame-Options?
Clickjacking
Play around a bit and check out the various vulnerabilities the scanner has found. Soon, you will find what you are looking for under the medium-severity vulnerability called Web Application Potentially Vulnerable to Clickjacking.
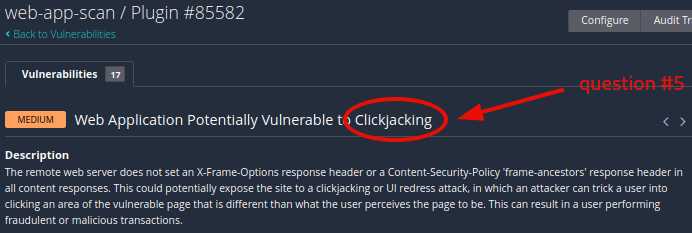
Figure 34: Full name for the medium vulnerability
This marks the end of this room. Check out the next room in the module about Hydra, and learn how to brute-force and obtain website credentials.